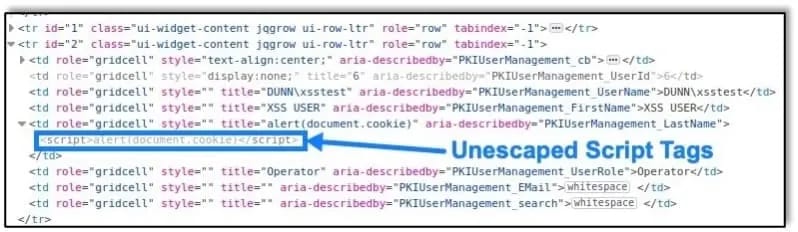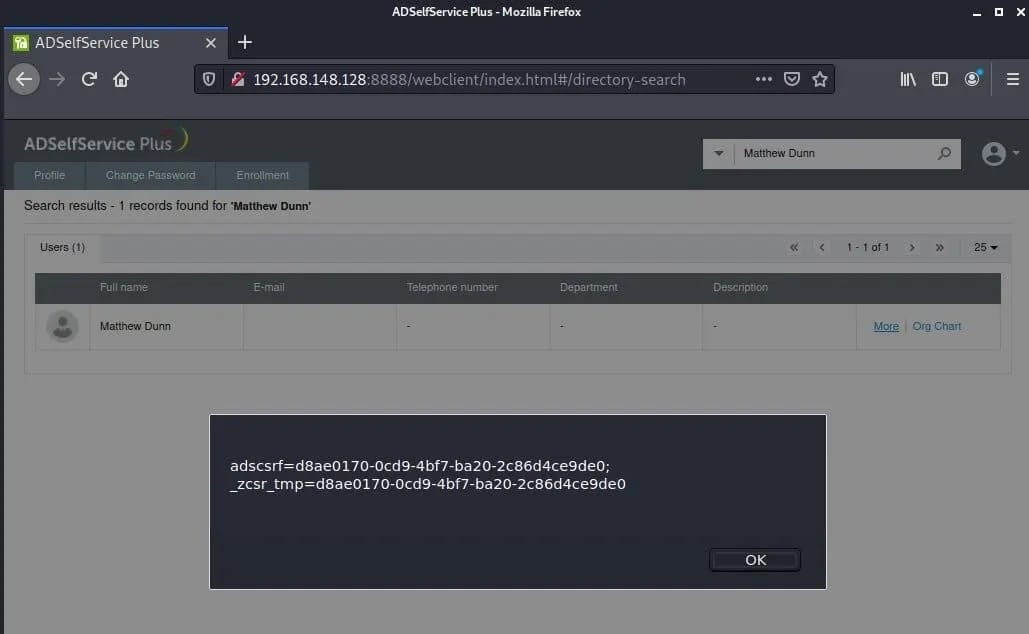

CVE-2022-24681: ManageEngine AD SelfService Plus Stored Cross-Site Scripting (XSS)
Raxis’ Matt Dunn continues his prolific discovery of new CSS CVEs. This one affects ManageEngine AD SelfService Plus Stored Cross-Site Scripting.
Discover expert insights on the latest exploits, penetration testing tactics, and real-world vulnerabilities to strengthen your cybersecurity defenses.
Raxis’ Matt Dunn continues his prolific discovery of new CSS CVEs. This one affects ManageEngine AD SelfService Plus Stored Cross-Site Scripting.
In this post, Raxis VP Brad Herring explains how web proxy tools can turn even simple buttons and check-boxes into avenues for an attack.
In this second in a series, learn how to perform Cross-Site Scripting (XSS) attacks such as filter evasion and sideloading content.
In this blog post, Raxis lead penetration tester Mark Fabian discusses broken access control and why it’s the most prevalent issue among the OWASP Top 10.
The latest draft of the OWASP Top 10 has been released. Though injection is #3, Raxis’ Matt Dun explains why that doesn’t mean the threat is any less severe.
Raxis’ Lead Penetration Tester Matt Dunn discovers another cross-site scripting vulnerability in Zoho’s MangeEngine Key Manager Plus (CVE-2021-28382).
Raxis lead penetration tester Matt Dunn has uncovered a new cross-site scripting vulnerability in Manage Engine AD Self Service Plus (CVE-2021-27956). Find out more here.
LDAP passback exploits are easy when companies fail to change default passwords on network devices or fail to assign a password at all. If you connect it, you must protect it.
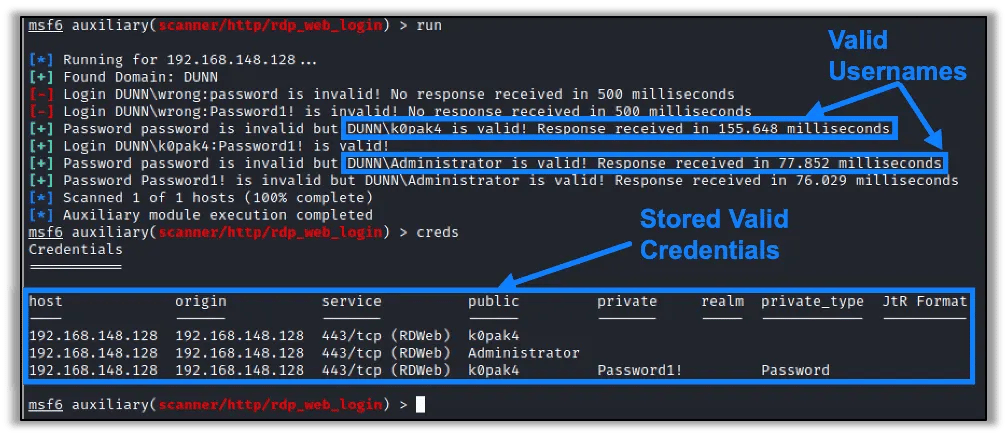
Raxis team member Matt Dunn has uncovered a vulnerability in Microsoft’s Remote Desktop Web Access application (RD Web Access). Learn more in this blog article.
Raxis’ penetration testing team demonstrates how to conduct a mousejacking attack to gain access as part of a penetration test.
A new nationwide cyberattack appears to be targeted at U.S. based hospitals, clinics, and other health care facilities. Healthcare on heightened alert.
We’re conditioned to be helpful and accommodating. That’s why tailgating works so well for hackers. The Raxis penetration testing team shows how.
83 posts in Exploits.