Raspberry Pi Planted in Failed ATM Heist
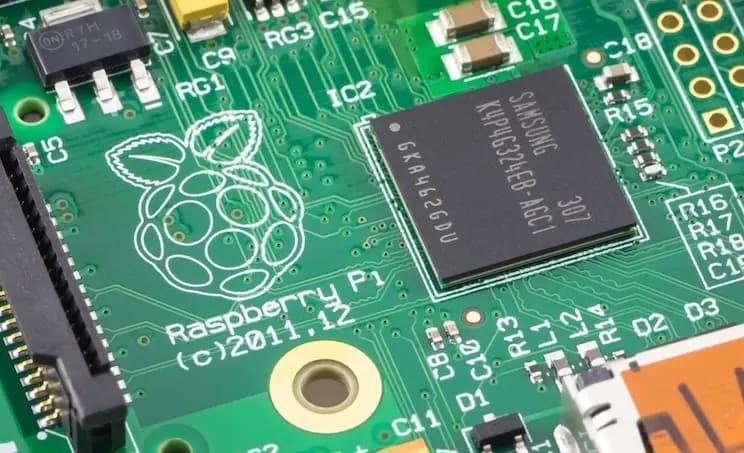
Raxis CTO Brian Tant discusses the Raspberry Pi used in a recent ATM heist and how Raxis uses the same type of device in our pentesting.
Real skill leaves evidence. Your examiner will know the difference.
Financial Sector Threat Data
Financial institutions are among the most targeted sectors and the most examined. The breach data says where the paths in are: a vulnerability nobody patched, a vendor nobody tested. We follow those paths by hand and show you what they reach.
Second only to healthcare, and well above the $4.99M average across all industries.
Source: IBM Cost of a Data Breach 2026
Now the most common way in, ahead of stolen credentials.
Source: Verizon DBIR 2026
Up 60% in a year. Core processors, fintech integrations, and SaaS vendors are part of your attack surface.
Source: Verizon DBIR 2026
A scanner report won’t satisfy an FFIEC examiner, and it won’t find the chained exploits, business logic flaws, and transaction manipulation paths real attackers use. A Raxis engineer tests by hand, the way an adversary would, and the report shows the path.
Online banking portals, mobile apps, payment APIs, and wire transfer systems handle customer NPI, and network-only testing misses the application-layer flaws where breaches happen. We test the full transaction path, from authentication to fund movement.
Segmentation between core banking systems, corporate networks, branch infrastructure, and customer-facing environments only matters if it holds under attack. If nobody attempts lateral movement, you don’t know that it does. We attempt it.
The FTC Safeguards Rule under GLBA mandates annual penetration testing and semi-annual vulnerability assessments for non-bank institutions, NYDFS Part 500 requires annual internal and external testing, and FFIEC and NCUA examiners expect risk-based testing regardless.
Every financial regulator asks for testing differently.
| Regulator / Rule | Who It Covers | What It Requires |
|---|---|---|
| FTC Safeguards Rule (GLBA, 16 CFR 314.4) | Non-bank financial institutions: mortgage and auto lenders, brokers, advisors, tax preparers | Annual penetration testing and semi-annual vulnerability assessments, unless you run continuous monitoring |
| NYDFS Part 500 (500.5, amended November 2023) | NY-licensed banking, insurance, and financial services entities | Annual internal and external penetration testing by a qualified party, plus automated vulnerability scanning |
| FFIEC guidance | Banks and thrifts examined by OCC, FDIC, and the Federal Reserve | Risk-based internal and external penetration testing, including social engineering. Since the CAT retired in August 2025, examiners look to NIST CSF 2.0 and the CRI Cyber Profile |
| NCUA (Part 748 / ISE) | Credit unions | Scales by asset size: SCUEP, CORE, and CORE+, with CORE+ covering penetration testing of wireless, applications, and firewall rules |
| PCI DSS v4.0.1 (11.4) | Anyone handling cardholder data | Annual internal and external penetration testing, segmentation testing, and retesting of fixes (PCI penetration testing page) |
One Raxis engagement produces evidence mapped to every row that applies to you. The examiner gets the path, the proof, and the fix, not a control checklist with our logo on it.
SCUEP (under $50M) needs documented testing fundamentals, CORE expects internal and external vulnerability scanning and penetration testing, and CORE+ adds wireless testing, application testing, firewall rule review, and core conversion testing. We scope to your ISE tier.
Account records, loan applications, and share draft data are Nonpublic Personal Information under GLBA and Part 748. We test every path to it: member-facing online banking, third-party core processors, branch networks, and the segmentation between them.
Senior, OSCP-certified engineers attack your systems by hand, the way a real crew would. Tools speed the reconnaissance. The engineer finds the path and proves it.
Evidence mapped to GLBA, FFIEC, NYDFS Part 500, PCI DSS, and SOX in a single report your examiner can follow.
Online banking portals, mobile apps, payment APIs, wire transfer and ACH systems, ATM environments, SWIFT-connected infrastructure, and third-party fintech integrations, tested end to end.
Proof-of-concept exploits, business impact, and prioritized remediation in Raxis One, written by the engineer who found them. No 200-page scanner dumps.
Lateral movement and privilege escalation show whether a compromised branch workstation can reach core banking systems, customer NPI, or transaction infrastructure. When we get there, we show you the path.
Annual testing is the minimum. Raxis Attack PTaaS keeps testing as releases, vendors, and integrations change, with real-time results and retesting of every fix.
Written by the Raxis engineers who run these tests, from real engagements and research.
Raxis CTO Brian Tant discusses the Raspberry Pi used in a recent ATM heist and how Raxis uses the same type of device in our pentesting.
The FTC has finalized changes to the GLBA Safeguards Rule. Here’s our take on how they are likely to affect financial institutions’ cybersecurity posture.
A hands-on attack on your banking systems, digital platforms, internal networks, and supporting infrastructure, done by a senior engineer the way an adversary would do it. It finds the exploitable paths before an attacker does and produces the evidence GLBA, FFIEC, NYDFS, and PCI DSS examiners expect.
Online banking platforms, mobile banking applications, payment APIs, wire transfer and ACH systems, ATM environments, internal and external networks, core banking system boundaries, wireless infrastructure, branch network segmentation, and third-party fintech integrations.
The GLBA / FTC Safeguards Rule, FFIEC IT Examination Handbook guidance, NYDFS Part 500 Cybersecurity Regulation, PCI DSS v4.0.1, and SOX internal control requirements. With the FFIEC CAT retired, findings also map to NIST CSF 2.0, CISA's Cybersecurity Performance Goals, or the Cyber Risk Institute's Cyber Profile.
The FTC Safeguards Rule and NYDFS Part 500 require annual testing. Banks and credit unions follow the Interagency Guidelines, FFIEC guidance, and NCUA requirements: risk-based testing at least annually and after significant changes. Many use Raxis Attack for continuous coverage between exams.
We work inside rules of engagement built for financial environments: agreed testing windows, no destructive testing against production transaction systems, and a stop-work contact on both sides. Live testing is never zero risk, so we won't tell you it is. We will tell you exactly what we plan to do before we do it, and we stop when you say stop.