Cool Tools: Ludus for Quick and Easy Testing Labs
To truly test the way a hacker would, you use specialized scripts. Scripts found in the wild need to be tested first, and Ludus lets you setup the perfect lab.
Discover expert-led penetration testing insights, real-world attack simulations, and best practices to uncover vulnerabilities and strengthen your security.
To truly test the way a hacker would, you use specialized scripts. Scripts found in the wild need to be tested first, and Ludus lets you setup the perfect lab.
Raxis is now verified for Red Team Access in Anthropic’s Cyber Verification Program. That gives our engineers Claude Mythos, Anthropic’s newest frontier model, cleared for authorized penetration testing.
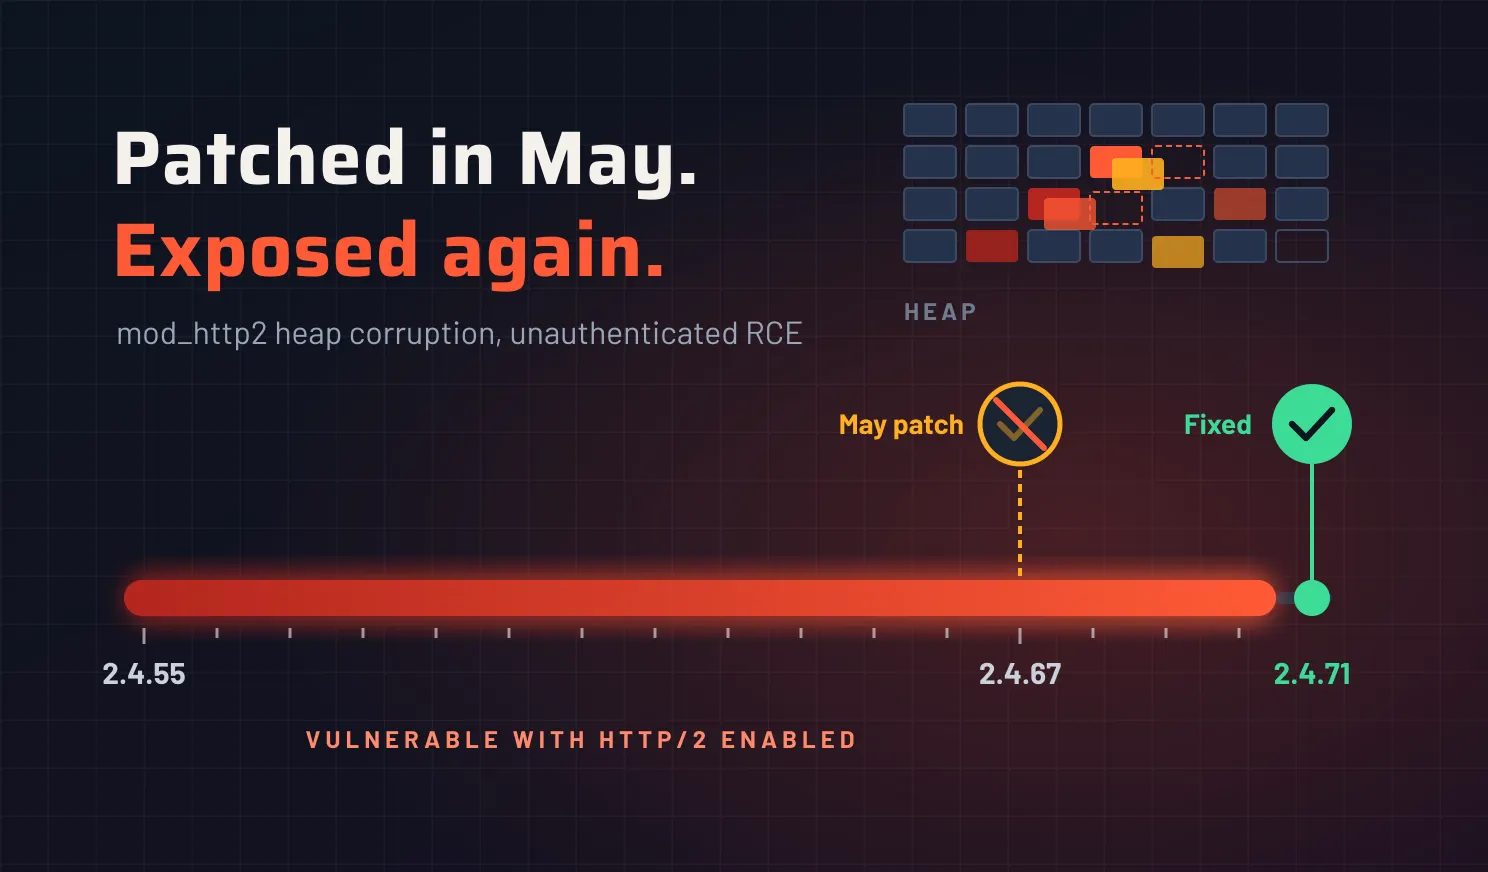
A critical Apache HTTP/2 flaw lets unauthenticated attackers run code on servers, even ones patched in May. Learn how to confirm exposure and mitigate it.
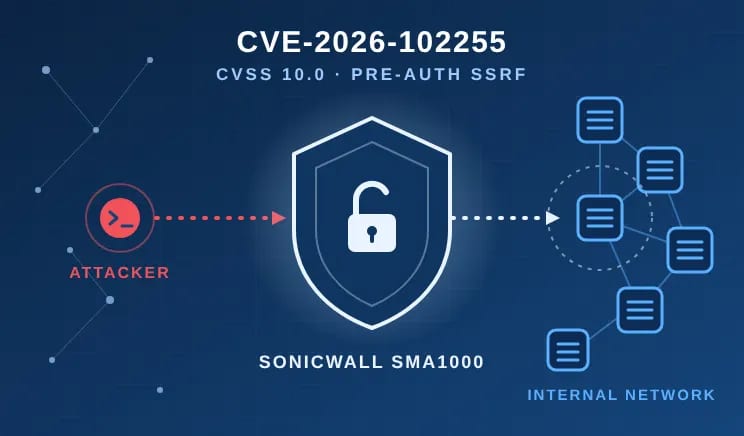
CVE-2026-102255 is a CVSS 10.0 SSRF flaw in SonicWall SMA1000 appliances. Attempts began two days after disclosure. Learn why patch windows must shrink.
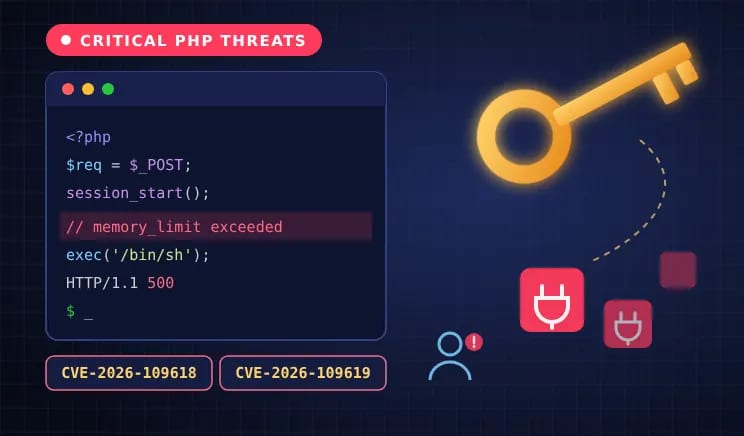
Patch PHP2Shell (CVE-2026-109618, CVE-2026-109619) and remove stolen UpdraftCentral keys. Raxis explains how to check exposure and fix both PHP threats.
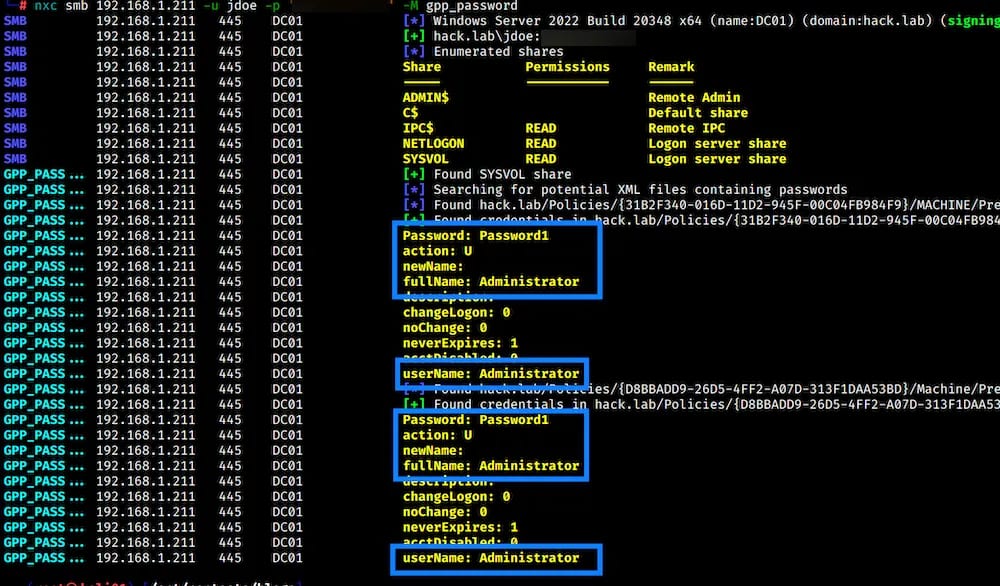
Learn how NetExec (NXC) modules speed up internal pentests. Scottie Cole covers GPP passwords, LAPS, Zerologon checks, and coerce_plus with example commands.
The French supermarket hack exploited unpatched, internet-facing Danfoss controllers. Learn why OT security gaps like this persist and how to close them.
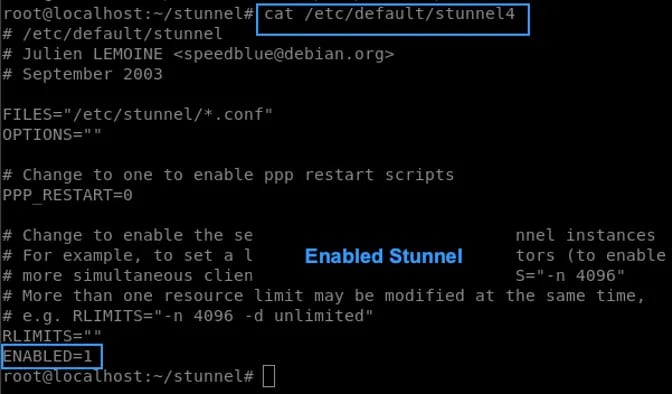
Pentesters often need to bypass Deep Packet Inspection (DPI), network IPS, and SOC detection by disguising network traffic. Learn how stunnel does just that.
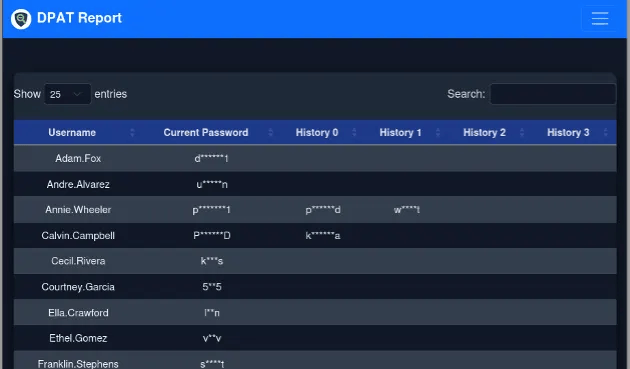
Learn how to use the Domain Password Audit Tool (DPAT) that helps you discover if policies are bypassed and if new policies need to be in place.
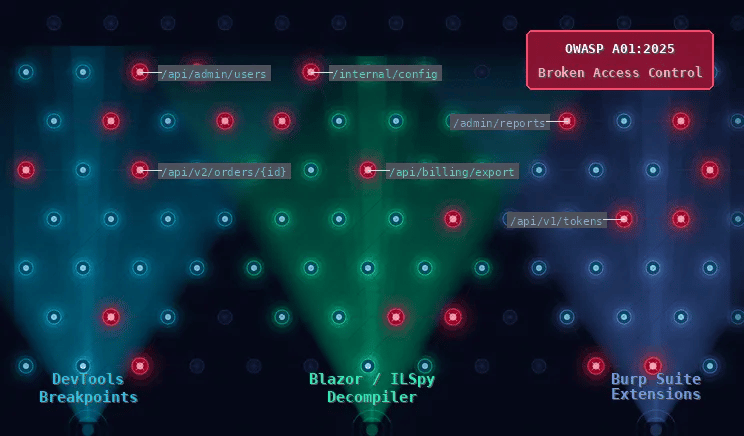
Broken Access Controls is at the top of the OWASP Top 10. The difficulty is finding each instance to test. Learn 3 ways to enumerate API endpoints thoroughly.
Operational Technology pentesting is highly specialized and needs to be performed by experienced OT testers. Learn how to choose the best pentest company.
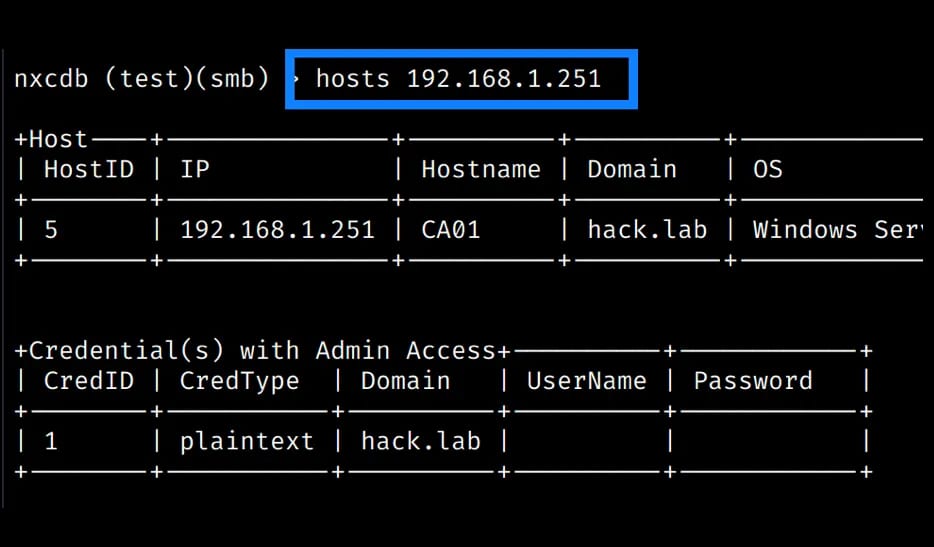
Principal Pentester Scottie Cole continues his NetExec series with nxcdb, the database that automatically stores key info like hosts and creds while you hack.
82 posts in Penetration Testing.