External Networks
Continuous testing of your internet-facing infrastructure. Find exploitable vulnerabilities before attackers reach them.
Tested in March. Breached in November.
A point-in-time pentest is a snapshot of the build that existed that week. Every release after it is untested. Raxis Attack keeps a senior engineer on the scope all year.
Annual pentest
One test. The rest of the year on trust.
Raxis Attack
A senior engineer on the scope all year.
Nothing replaces skill. An illustrative year. The months are the order of events, not a schedule.
Agile teams push updates weekly or daily. A point-in-time pentest only validates the version that existed during the engagement, so coverage expires the day your environment changes, and every untested release is a risk.
Some vendors sell automated scanning with a dashboard and call it PTaaS. A scan flags known issues; it cannot chain weaknesses, abuse business logic, or prove real impact. Raxis Attack keeps a human tester at the center, and the findings show it.
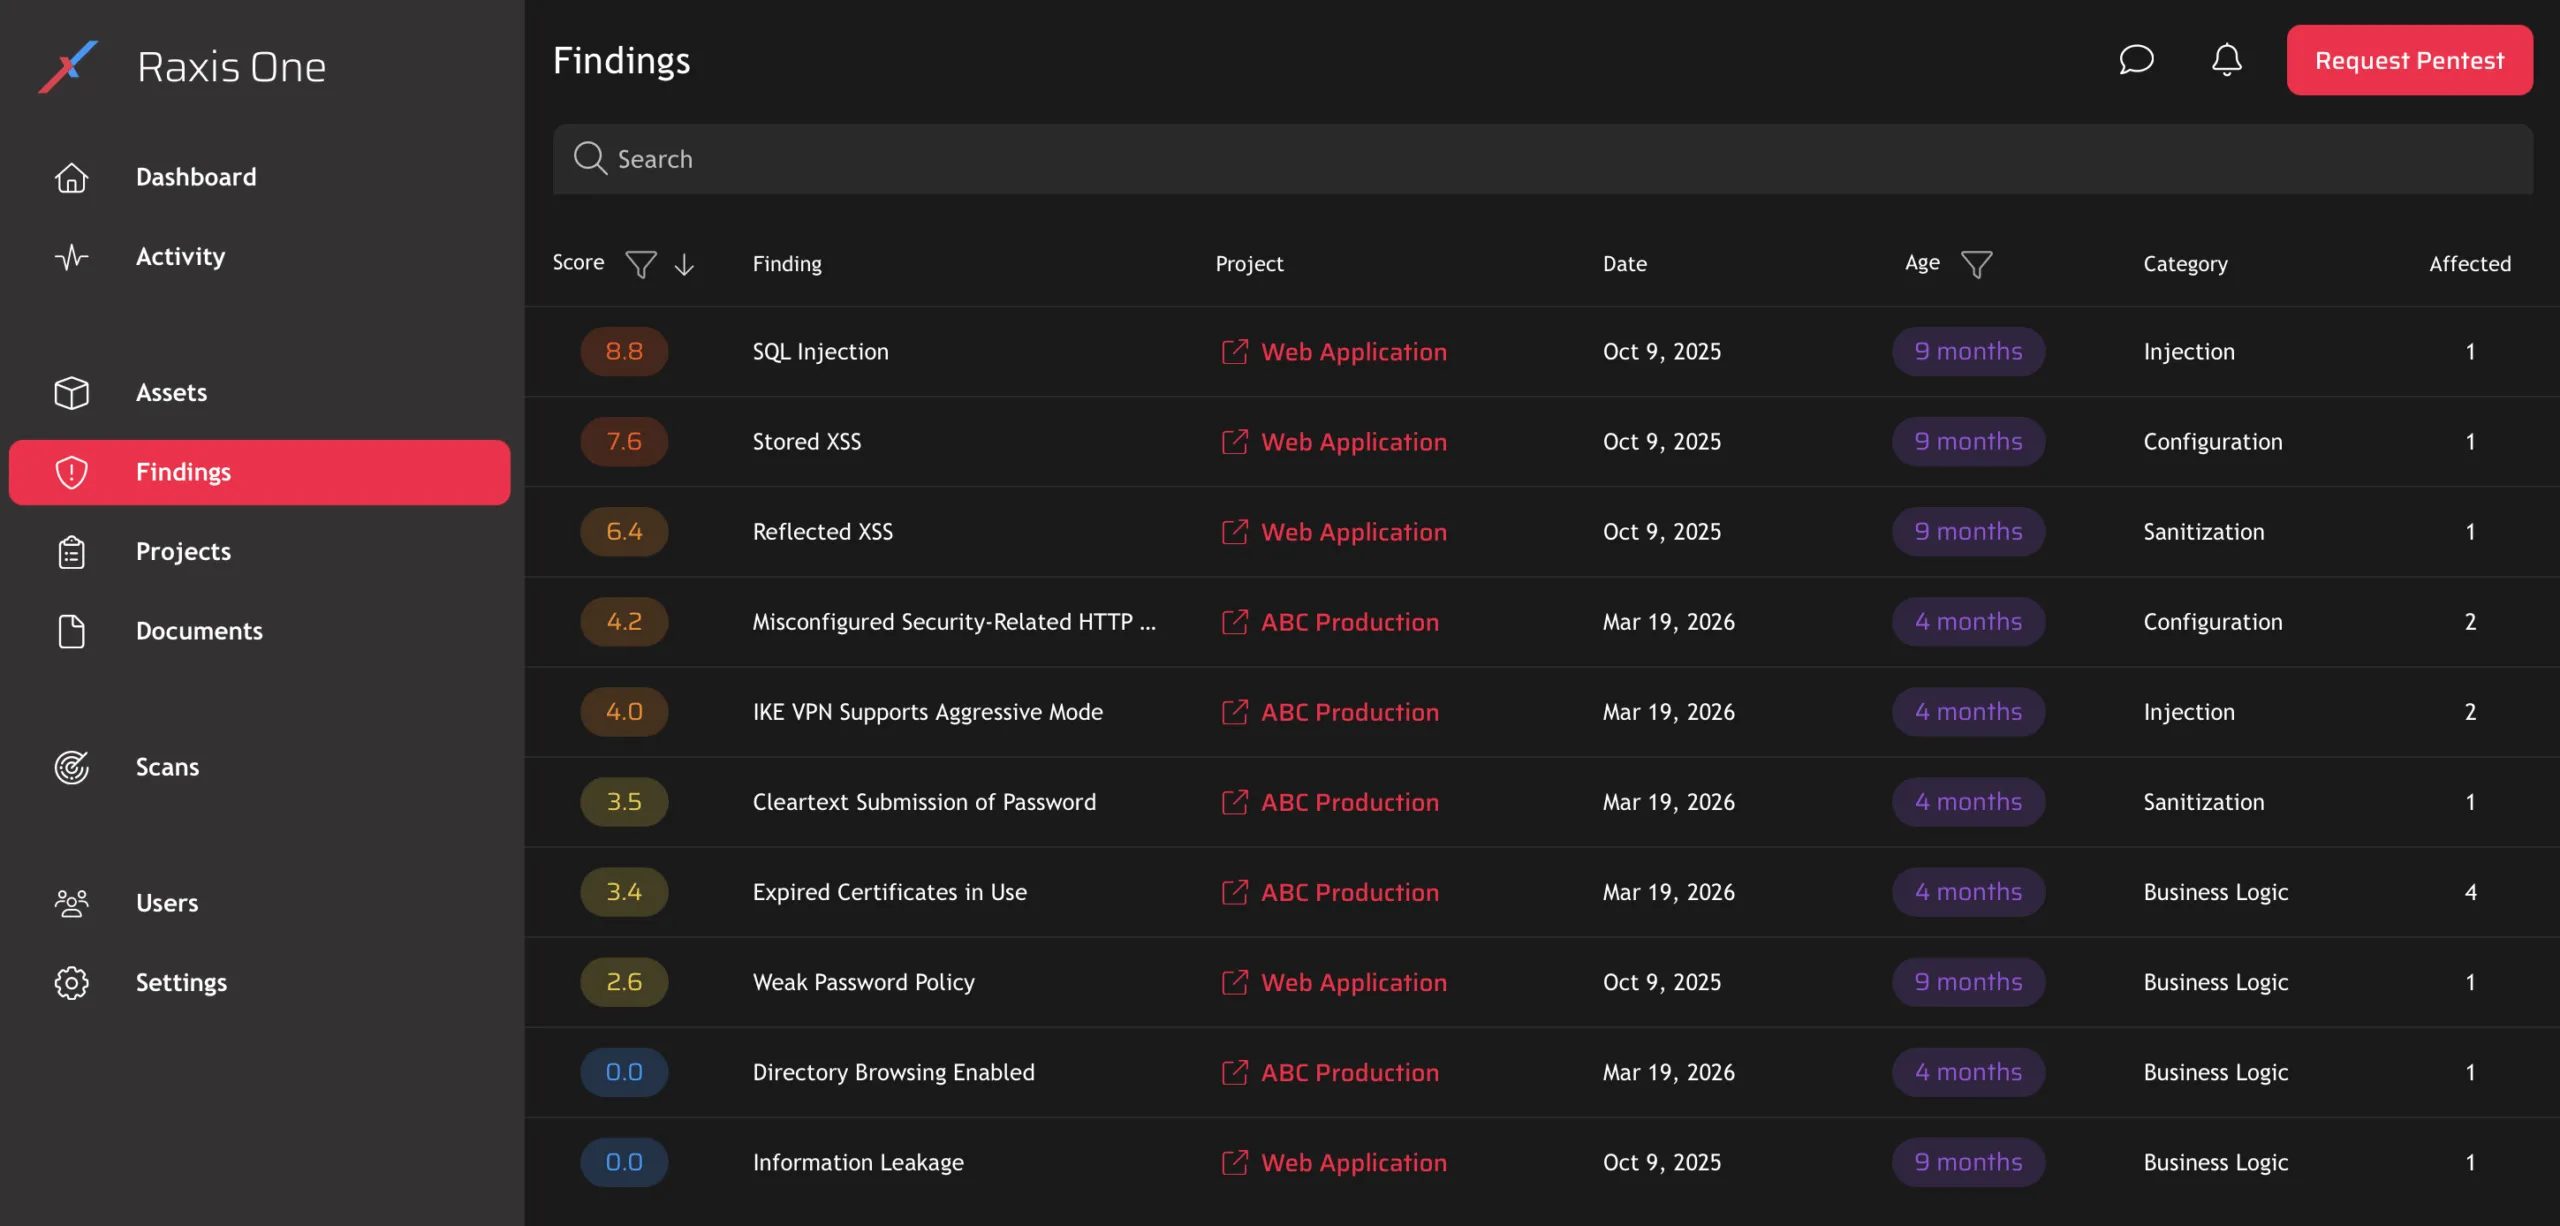
No waiting weeks for a PDF. Validated findings reach your team in real time through Raxis One, with the detail to reproduce, prioritize, and fix while testing is still under way.
The same engineers running your continuous testing have published multiple CVEs in platforms like ManageEngine, PRTG, and Rock RMS.
Raxis holds a SOC 2 Type II examination covering the Security Trust Services Criteria. See the details in the Raxis Trust Center.
Findings appear in Raxis One from our certified engineers, complete with proof-of-concept exploits and attack storyboards.
US-based penetration testers lead every Raxis Attack engagement. We never offshore your testing.
Test as often as you need, after every sprint, release, or infrastructure change. We retest every fix as many times as needed and confirm it holds. No per-test fees and no retest fees, ever.
No ticket queues. No AI chatbots. Raxis Attack gives you a direct line to a US-based pentester working your engagement. Ask questions, discuss findings, and collaborate on fixes.
Connect Raxis One to GitHub, GitLab, Jira, Slack, and Teams. Findings flow into your existing workflows, so developers see vulnerabilities in the tools they already use every day.
AI-powered tools accelerate reconnaissance and expand coverage. Engineers decide what to try next, chain the exploits, and write every finding. You’ll know the report wasn’t AI generated.
Every vulnerability appears in the Raxis One portal as it is discovered, with proof-of-concept screenshots, risk ratings, and remediation guidance. No waiting for a final report.
Raxis Attack meets the recurring penetration testing requirements behind PCI DSS, HIPAA, SOC 2, ISO 27001, CMMC, and more. Generate audit-ready reports from Raxis One on demand. See how each framework maps to Raxis Attack PTaaS.
Continuous testing of your internet-facing infrastructure. Find exploitable vulnerabilities before attackers reach them.
Simulate insider threats and compromised endpoints across internal networks and AWS, Azure, and GCP environments.
Manual exploitation of authentication flaws, business logic errors, injection vulnerabilities, and session management weaknesses, well beyond OWASP Top 10 scanning.
Wi-Fi, Bluetooth, and radio. Advanced attack techniques automated scans miss.
REST, GraphQL, SOAP, and gRPC. Test for broken authentication, authorization bypasses, and data exposure.
Ongoing phishing, vishing, and onsite assessments that surface human and process gaps, paired with targeted training.
Continuous testing for LLM apps, RAG pipelines, AI agents, and system prompts. Every model swap, prompt change, and new tool introduces fresh risk.
iOS and Android apps tested at the pace you release them. Catch insecure storage, weak encryption, and backend flaws before they hit the store.
Salesforce environments drift constantly. We monitor sharing rules, custom objects, permission sets, and integrations for the misconfigurations that expose customer data.
Predictable annual spend covers recurring testing throughout the term. Unlimited access costs typically 2 to 3 times a traditional penetration test per year.
Annual subscription is typical; multi-year commitments (1–3 years) improve planning, budgeting, and total value.
Validate after code changes, releases, or infra updates without negotiating new projects. Retest fixes as often as needed.
More validation cycles for the spend. Continuous coverage beats the cost of repeated standalone tests.
Prices start at $25K for one year depending on the scope. Three year deals often work out as better value per year.
01
We define your scope, connect Raxis One to your DevSecOps toolchain, and establish ongoing access. Your dedicated engineer learns your environment from day one.
02
AI-powered tools and manual OSINT continuously monitor your attack surface for new exposures, configuration changes, and emerging vulnerabilities as your environment evolves.
03
Our testers manually exploit discovered vulnerabilities, chaining weaknesses, escalating privileges, and demonstrating real impact with proof-of-concept evidence.
04
Findings appear in Raxis One as they’re confirmed. Prioritized by risk, with screenshots, attack narratives, and specific remediation steps your team can act on immediately.
05
Your team fixes. We verify. Communicate directly with your assigned engineer through the portal, get questions answered, and confirm each vulnerability is properly closed.
06
New code deployed? Infrastructure changed? Trigger another round on demand. Raxis Attack adapts to your release cadence, not the other way around.

Our stories are based on real events encountered by Raxis engineers. Some details have been altered or omitted to protect customer identities.
Our customer is a large enterprise with thousands of IP addresses and hundreds of services. With this large attack surface in place, they initially engaged Raxis for traditional internal and external network penetration tests. Pleased with the information they obtained there, they rolled up their sleeves and began knocking out critical and high risk remediations. But they didn’t stop there. These folks know that the cybersecurity threat landscape is always changing, so they made the leap to Raxis Attack.
Continuous, human-led PTaaS replaced the annual scramble, and the Raxis One dashboard became their daily command center. Now, the moment a Raxis tester confirms a finding, it materializes on their dashboard with a proof-of-concept screenshot, a risk-rating, an attack narrative, and prescriptive remediation steps. When something new appears, they don’t wait. They use the chat with a pentester feature to work directly with the Raxis pentest team if they have questions, and they remediate the findings in real time. Broadcast poisoning, once a big vector in their environment, is now a no-go for attackers. Their team is ready to squelch each new vulnerability as soon as it appears.
The result? A once-vulnerable environment is now one of the hardest targets we test. Critical and high risk findings are rare and are retired in days when they do appear. The gap that annual testing used to leave wide open has effectively vanished. This is what continuous penetration testing looks like in practice: real testers, real exploits, real-time findings, and a security team that stays one step ahead because they never stop hearing from the people trying to break in.
PTaaS is a continuous, platform-based approach to penetration testing that replaces one-and-done annual assessments with ongoing, on-demand testing. Raxis Attack combines unlimited human-led testing with AI-augmented automation, delivered through the Raxis One portal with real-time findings and DevSecOps integration.
A traditional penetration test is a point-in-time assessment. You test once, get a report, and wait until next year. PTaaS provides continuous testing that keeps pace with your development cycles, with real-time findings and unlimited retesting as your environment evolves.
External networks, internal networks, cloud environments, web applications, APIs, wireless networks, and social engineering. All under a single subscription with unlimited testing.
Raxis One connects to GitHub, GitLab, Jira, Slack, and Microsoft Teams. Findings flow into your existing tools so developers and security teams can remediate without leaving their workflow.
Yes. Every Raxis Attack engagement includes direct access to your assigned engineer through the Raxis One portal. No ticket queues, no chatbots. Real-time collaboration with the person testing your systems.
Yes. Every assessment follows NIST SP 800-115 and supports PCI DSS, HIPAA, SOC 2, GLBA, ISO 27001, CMMC, and other frameworks. Reports are audit-ready and generated directly from the platform.
Unlimited. Test after every sprint, release, or infrastructure change. Target a single application, a network segment, or your entire scoped environment, as frequently as you need. Concurrent testing on the same scope isn't supported.
Raxis Attack is continuous PTaaS with unlimited testing, DevSecOps integration, and real-time findings. Raxis Strike is a focused, point-in-time engagement, ideal for annual compliance, pre-launch validation, or targeted assessments. Both use the same team and the same AI-augmented methodology.
No. Automated scanning is one component. Every Raxis Attack engagement is driven by certified testers who manually exploit vulnerabilities, chain attack paths, and demonstrate real business impact. Same depth as a traditional Raxis pentest, delivered continuously.