Raxis Attack
Penetration Testing as a Service
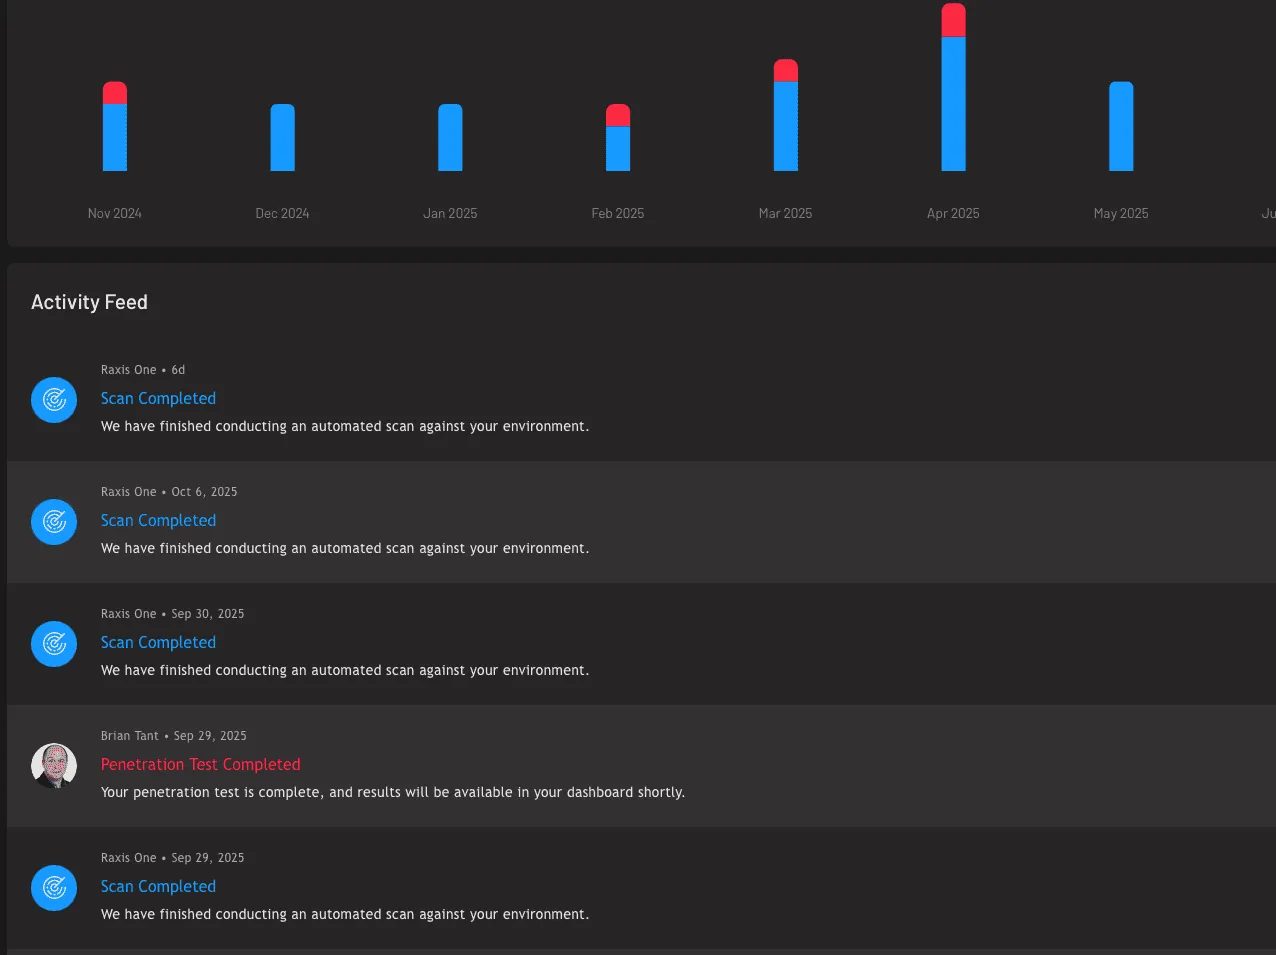
Unlimited manual penetration testing powered by Raxis One, every release, all year long.
Manual testing by senior U.S. engineers who publish CVEs.
Penetration Testing as a Service
Unlimited manual penetration testing powered by Raxis One, every release, all year long.
Point-in-Time Penetration Testing
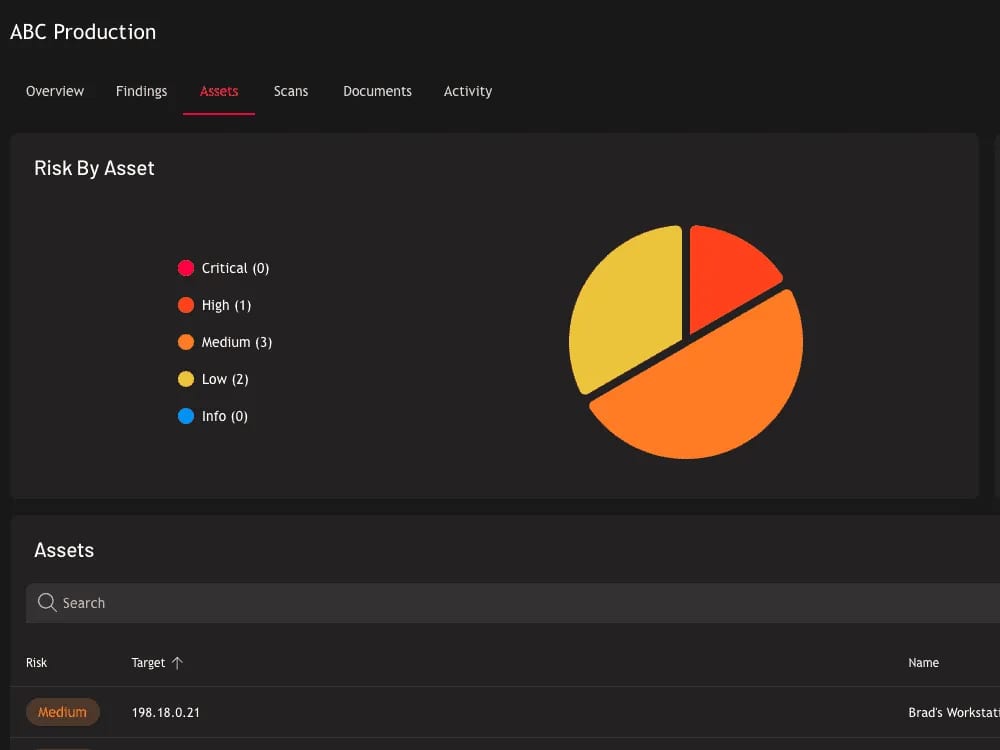
Deep human-led manual testing backed by AI-augmented automation, focused on your defined scope.
A checkbox vendor hands you a list of Lows. Raxis hands you the real attack path.
Low 3.1
IDs increment by one.
/records/1001, 1002, 1003
Exploited
Low 3.7
No throttle. Full sweep.
12 minutes. 40,000 IDs.
Exploited
Low 3.1
Any token. Any object.
Ownership never checked.
Exploited
Critical 10.0
Every record. Every tenant.
CWE-200 · CVSS 10.0
Exfiltrated
0 Critical · 0 High · 3 Low
Checkbox Vendor
Pass with low severity findings.
A list of Lows. No path. No proof.
1 Critical · 0 High · 3 Low
Critical finding, with customer data exposure.
You get the attack path. Not just a list of low findings.
A single low-sev finding rarely ends there. We chain misconfigs, weak creds, and app flaws into the exact path to your crown jewels.
Your stack is one of a kind, so our attacks are too. We build custom scripts and payloads tuned to your internet facing, apps, cloud, and APIs.
Automation handles the grunt-work recon. Our pentesters validate exploitability, test business logic, and eliminate the scanner noise.
You get a clear picture of what an attacker could pull off, ranked by real risk, with steps to reproduce and remediate each one. Patch the worst, sleep better.
The pentester on your scope call is the one breaking in. And the one retesting your fix.
We publish CVEs. When something looks off, we dig until we understand it.
After you remediate, we retest to confirm the fix actually holds, so you close the loop instead of guessing.
We move from scope call to kickoff quickly. Findings land in one to two weeks for most scopes, so you fix things while they’re still fresh.
See vulnerabilities in Raxis One the moment we confirm them. No waiting around for a PDF.
We’ve been breaking into things since 2011. The experience shows.
Certified, US-based testers, reports your auditors accept. Visit the Raxis Trust Center.
Expert-led assessments across every layer of your technology stack.
We map the path from one domain user to Domain Admin through Kerberoasting, delegation abuse, and AD CS flaws.
APIs are heavily targeted and rarely tested. We find broken authentication, data exposure, and authorization flaws.
We test LLM apps, RAG pipelines, AI agents, and system prompts for prompt injection, data leakage, and abuse paths traditional pentests miss.
We test blockchain and crypto platforms for authentication flaws, key management weaknesses, and misconfigurations.
We test cloud environments (AWS, Azure, GCP) for privilege escalation, identity misconfigurations, and exposed keys and roles.
We probe your perimeter the way a real attacker would, finding the weaknesses that give them a foothold.
We test internal networks for lateral movement, privilege escalation, and the misconfigurations that lead to domain-wide access.
We find vulnerabilities across the full IoT stack: hardware, firmware, cloud APIs, and wireless protocols.
We test iOS and Android apps for insecure storage, weak encryption, and backend vulnerabilities.
We test SCADA, ICS, and industrial control systems for exploitable vulnerabilities without disrupting operations.
Targeted phishing, spear phishing, and pretexting that show how your team responds under real attack.
Our Red Team breaches your facilities through tailgating, badge cloning, lock picking, and pretexting.
Salesforce holds your most sensitive customer data. We find misconfigured sharing rules, exposed APIs, and weak access controls.
Decompile desktop apps to find hardcoded secrets, insecure local storage, and bypass client-side controls.
Manual testing for logic flaws, authentication bypasses, and injection vulnerabilities that automated scanners miss.
Our Transporter hardware deploys onsite to find rogue access points, weak encryption, and misconfigurations that bypass your perimeter.
A checkbox pentest satisfies your auditor. A Raxis penetration test shows you where you’re actually exposed.
A U.S. breach now runs $10.22 million and takes 241 days to catch and contain (IBM’s 2025 report). Plenty start with a known vulnerability nobody bothered to validate.
Based on our proven process, every critical finding ships with a working proof-of-concept and a step-by-step storyboard of the full kill chain. Sometimes, this means chaining three Low findings into a Critical.
You get prioritized fixes with the exact steps to close each gap, ranked so your engineers know what to hit first.
Raxis supports PCI DSS Requirement 11.4 with manual exploitation, segmentation validation where applicable, and the documented testing methodology QSAs expect under v4.0.
Supports the Security Rule’s risk analysis and evaluation expectations, including §164.308(a)(1)(ii)(A) and §164.308(a)(8), with web application and network penetration testing that surfaces real ePHI exposure.
Produces auditor-ready evidence for the security Trust Services Criteria, showing your controls hold up to real exploitation rather than policy review alone.
Delivers periodic penetration testing and vulnerability assessment evidence for FTC Safeguards Rule testing expectations under 16 CFR 314.4(d).
Delivers technical vulnerability testing evidence aligned with ISO/IEC 27001:2022 Annex A 8.8 for management of technical vulnerabilities.
Supports DoD contractors protecting CUI with penetration testing evidence aligned to CMMC 2.0, NIST SP 800-171 objectives, and advanced Level 3 expectations where applicable.
Our methodology follows NIST SP 800-115, the federal technical guide to security testing and assessment.
Supports Article 32(1)(d)’s requirement to regularly test and evaluate the effectiveness of your security measures, with risk-based testing scaled to your processing.
Manual exploitation built on the OWASP Web Security Testing Guide, going beyond automated vulnerability scanning.
AI application testing aligned to the OWASP Top 10 for LLM Applications and the MITRE ATLAS adversarial framework for AI-enabled systems.
Real-world exploit validation that helps demonstrate reasonable security practices under Section 5 of the FTC Act.
Supports CIS Critical Security Control 18 with penetration testing that validates whether defenses work as intended.
Provides real exploitation evidence that informs NIST CSF 2.0 risk management across Govern, Identify, Protect, Detect, Respond, and Recover outcomes.
Supports FedRAMP penetration testing requirements for cloud service providers, following FedRAMP Penetration Test Guidance and required attack vectors.
Our penetration tests follow industry standards to ensure comprehensive coverage.
Zero prior knowledge. Simulates an external attacker discovering and exploiting your systems from scratch.
Partial information, typically user credentials or limited architecture details, simulating a compromised account or insider threat.
Full transparency. Complete documentation, credentials, and source code access for the most thorough assessment possible.
“Raxis’ expertise, top-notch customer service, and attention to detail were impressive.”
“Raxis did an excellent job on fully testing this application.”
“They had a high level of professionalism and expertise.”
A penetration test is a controlled, authorized simulation of a real-world cyberattack against your systems. Unlike automated vulnerability scans, penetration testing uses manual exploitation techniques to demonstrate how an attacker could gain unauthorized access, escalate privileges, move through your network, and exfiltrate sensitive data. The result is a clear picture of your actual security risk, not just a list of theoretical vulnerabilities.
A vulnerability scan runs automated tools against your systems to identify known issues from a database. Penetration testing goes far deeper. Expert engineers manually exploit vulnerabilities, chain multiple weaknesses together, and simulate sophisticated real-world attacks to demonstrate actual business impact. Scans tell you what might be wrong. A penetration test proves what an attacker can actually do.
Raxis provides external network, internal network, cloud infrastructure, web application, API, mobile application, wireless, IoT, OT/SCADA, and full-scope red team penetration testing services. We also offer specialized testing for compliance frameworks including PCI DSS, HIPAA, SOC 2, GLBA, ISO 27001, and CMMC.
Raxis combines elite human expertise with AI-powered tools to accelerate discovery and expand attack surface coverage. Our optional AI augmentation speeds reconnaissance, identifies patterns, and surfaces hidden vulnerabilities, but testing is always led by certified engineers who chain exploits, assess business logic, and demonstrate real impact. We also develop custom tools and scripts tailored to each engagement. Your data is never used for AI training. We are also able to only use client-approved tooling if specified.
Raxis Strike is a comprehensive, point-in-time penetration test, ideal for annual compliance assessments or targeted security evaluations. Raxis Attack is our Penetration Testing as a Service (PTaaS) platform, delivering unlimited, continuous penetration testing with real-time findings and seamless integration into your development workflows through Raxis One.
Yes. The Raxis Research Team has discovered and published CVEs across enterprise platforms including ManageEngine and PRTG Network Monitor. This original vulnerability research reflects the depth of expertise our engineers bring to every engagement, they don't just run known exploits, they find new ones.
Timelines depend on scope and complexity. A focused external network or web application test typically takes 1–2 weeks. Larger engagements covering multiple systems, applications, and network segments may take 3–4 weeks. We provide a clear timeline during scoping.
Raxis penetration testing is designed to be safe and non-disruptive. Our methodology prioritizes system stability, and we coordinate closely with your team on timing and scope. Disruptions are extremely rare.
You receive a comprehensive report through the Raxis One portal with findings prioritized by severity, proof-of-concept exploit demonstrations, full attack storyboards, and specific remediation guidance. We also conduct a live debrief session to walk your team through every finding.
Yes. Every Raxis engagement includes remediation retesting to verify that vulnerabilities have been properly resolved, not just patched on paper.
Yes. If you're up against a deadline, tell us on the scope call and we'll work to get you scheduled sooner. Expedited engagements may carry an additional fee when meeting your timeline requires us to shift other work or add testers to the scope. We'll tell you before you sign anything, so there are no surprises on the invoice.