
Cool Tools Series: SCP
Raxis Lead Penetration Tester Nathan Anderson continues our Cool Tool Series with SCP for data exfiltration on internal network pentests and red teams.
Master penetration testing with Raxis “How To” tutorials. Get expert, step-by-step guides to uncover and fix vulnerabilities in your organization.
Raxis Lead Penetration Tester Nathan Anderson continues our Cool Tool Series with SCP for data exfiltration on internal network pentests and red teams.
Jason Taylor brings highlights reptyr in our Cool Tools series, showing how to take a long-running process, like an Nmap scan, and move it to a new screen.
So you got DA on your red team or internal network penetration test. Here are the five things that Principal Penetration Tester Andrew Trexler does next.
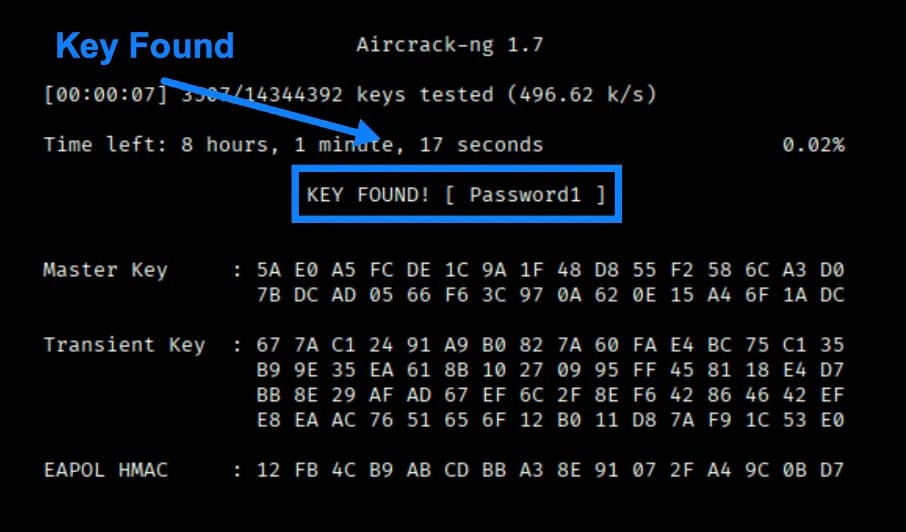
Principal Penetration Tester Scottie Cole continues our wireless series with the Aircrack-ng Suite, a set of tools for wireless pentest discovery and exploits.
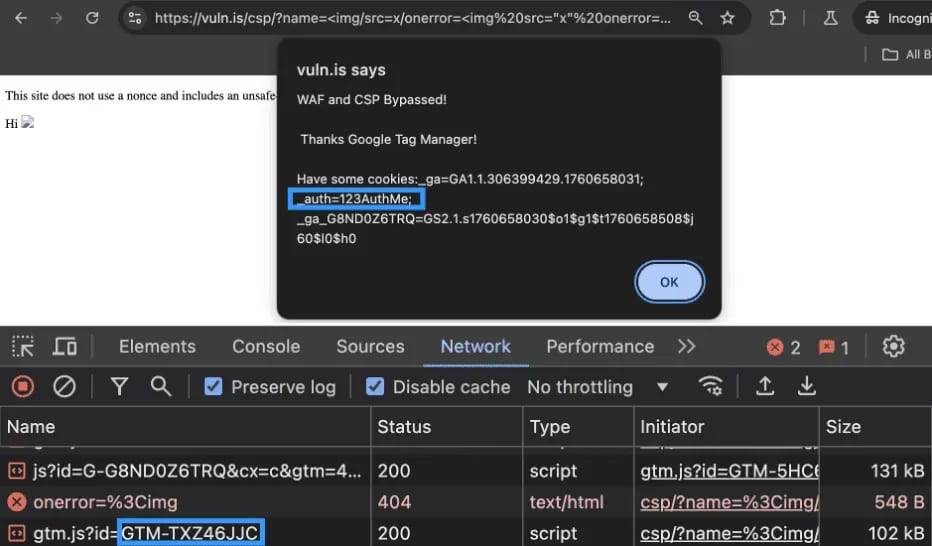
Ryan Chaplin takes an in-depth look at how attackers can use unsafe directives to bypass CSP, notably in Google Tag Manager, and how to remediate the issue.
Lead Penetration Tester Nathan Anderson is back with more PSE and red team tips, including tailgating, impersonating, and pretexts to gain onsite access.
Raxis’ Jason Taylor is back with a detailed tutorial on performing both manual and automated DNS exfiltration attacks for pentesting.
We reached into our vaults to bring you the final video in our cross-site scripting (XSS) series. Learn about cookie theft, website defacement, and CSRF attacks.
Raxis Lead Penetration Tester Jason Taylor’s in-depth tutorial explains setting up a server for DNS exfiltration. Check back next month to run the attack.
Lead Penetration Tester Nathan Anderson is back with more PSE and red team advice, this time looking into three tools he uses to clone badges and gain access.
Raxis Senior Penetration Tester Nate Jernigan discusses lateral movement in penetration testing and the methods and tools he uses when performing these attacks.
Lead Penetration Tester Nathan Anderson provides tips on using croc for secure data exfiltration just like he does on red team engagements.
69 posts in How To.