
Raxis Strike

Point-in-Time Penetration Testing
A traditional, scheduled internal penetration test with a defined scope and full report. Ideal for annual compliance testing.
One stolen password is all it takes. We test what happens next the way a real attacker would.
Phishing, stolen credentials, and rogue insiders put attackers behind your firewall every day. Most breaches start with a foothold, not a perimeter exploit.
Weak segmentation and legacy protocols let an attacker move from one workstation to domain admin in hours.
Once inside, attackers abuse the trust between accounts, systems, and services. We follow those same paths to show where they lead.
Kerberoasting, delegation abuse, and misconfigured permissions that turn a standard user account into domain admin.
We pivot between systems the way real attackers do, mapping how far one compromised host can reach.
We validate and exploit vulnerabilities by hand, chaining weaknesses to demonstrate real-world impact, not theoretical risk.
LLMNR poisoning, hash capture, and offline password cracking test your password policies where they matter most.
We verify that sensitive segments, including PCI cardholder data environments, are truly isolated from the rest of your network.
Outdated software, default configurations, and exposed internal services that give an attacker an easy next step.
A traditional, scheduled internal penetration test with a defined scope and full report. Ideal for annual compliance testing.

Continuous internal network pentesting through our PTaaS platform. Your environment is tested as it changes, not once a year.
Both are performed manually by senior US-based Raxis engineers holding certifications such as OSCP and OSCE.
A concise summary written for leadership and auditors.
Every finding includes a severity rating, reproduction steps, and clear remediation guidance.
A step-by-step narrative shows exactly how we got in and how far we could go.
We verify your fixes and deliver a clean final report at no extra cost.
LLMNR and NBT-NS responses hand us password hashes just for being on the network.
Service accounts with weak passwords that any domain user can request and crack offline.
Password policies that look fine on paper but fall to our cracking rigs in minutes.
Users and service accounts with local administrator access far beyond what their role needs, handing attackers easy privilege escalation.
Hosts running outdated software with public exploits available.
Flat networks where any workstation can reach domain controllers, databases, and the cardholder data environment.

Our stories are based on real events encountered by Raxis engineers. Some details have been altered or omitted to protect customer identities.
Banks tend to have mature perimeters, and their teams are often confident the inside is just as strong. Internal penetration tests exist to check that assumption.
During an internal engagement at a bank, our team recovered previously used credentials from an employee workstation. Testing those credentials carefully across systems led to domain access, and cracked password hashes produced logins that worked on employee workstations and the core banking system itself.
As a controlled proof of concept, we logged in as a teller to initiate a funds transfer, then approved it as a manager. We demonstrated it live for the bank, which used the Raxis report to drive immediate improvements to credential hygiene and access controls.
It is a test that starts from inside your network, the position an attacker reaches after phishing an employee, stealing a laptop, or plugging into a jack. From there our engineers do what a real intruder would: capture credentials, move between systems, escalate privileges, and see how close they can get to your most sensitive data.
An external test attacks your internet-facing perimeter from the outside. An internal test assumes the perimeter has already been crossed and measures what an attacker can do once inside. Most organizations need both: the external test to check the front door, the internal test to check what happens when someone gets past it.
A scan lists potential issues based on version numbers and known signatures. A Raxis internal pentest exploits them by hand, removes false positives, chains weaknesses together, and shows the real business impact of a breach. A scanner tells you a service is out of date; we show you the domain admin access it leads to.
At least once a year, and again after any significant change to your network, such as a merger, a new site, or a major infrastructure project. PCI DSS and most other frameworks expect an annual test. Continuous testing through Raxis Attack keeps you covered between point-in-time engagements.
Most internal tests run one to two weeks, including reporting. The main drivers are the number of live hosts, the number of physical locations, and whether segmentation testing is included. We give you a firm timeline before the engagement starts.
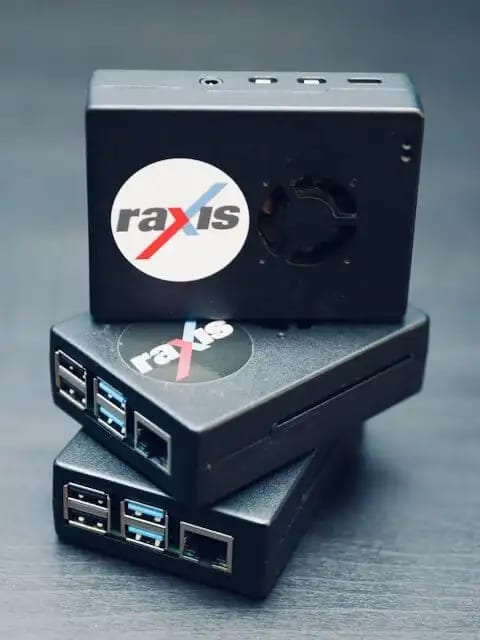
Your internal IP ranges, a point of contact, and a place to plug in our Transporter device. That is usually all it takes. There is no onsite visit and nothing to install on your workstations.
No. By default we start unauthenticated, with no account, to mirror an attacker who just gained a foothold. Many customers also ask for an assumed-breach test, where we start with a standard user account to see how far a phished employee's access would reach. We can run either or both.
It is very unlikely. We avoid disruptive exploits by default, flag fragile or legacy systems during kickoff, and can schedule sensitive testing inside a maintenance window if you prefer. Our goal is to prove risk, not to break production.
Yes. Segmentation validation fits naturally into an internal penetration test, confirming that your cardholder data environment is isolated from out-of-scope networks. PCI DSS requires this for segmented environments, and combining it with your internal test saves time and budget.
That is your call. Some customers stay quiet to test whether their SOC or MSSP detects and responds to our activity, which is a useful measure on its own. Others notify in advance to avoid alert fatigue. We plan the approach with you during kickoff.
We can. A Transporter at each site lets us test every location remotely, or we can focus on representative sites if your offices share a common build. We scope this with you based on how your network is segmented between locations.
A full report with an executive summary for leadership and auditors, detailed technical findings with severity ratings and reproduction steps, and an attack storyboard showing exactly how we moved through your network. You also get an attestation letter and a free retest to confirm your fixes. Everything is available in real time through Raxis One.
Scope is the main factor: the number of live internal hosts, the number of locations, and whether you add segmentation testing. Contact us for a quote sized to your environment.
Senior US-based Raxis engineers holding certifications such as OSCP and OSCE. No outsourcing, and no junior testers learning on your network.