
Cross-Site Scripting (XSS): Cookie Theft – Advanced Payloads
We reached into our vaults to bring you the final video in our cross-site scripting (XSS) series. Learn about cookie theft, website defacement, and CSRF attacks.
The Raxis Research Team is dedicated to staying ahead of the threat landscape. Our experts dig into emerging exploits, uncover hidden vulnerabilities, and develop resources that power our penetration testing engagements. By combining curiosity with technical precision, the team equips Raxis testers with cutting-edge intelligence to simulate real-world attacks and strengthen client defenses.
We reached into our vaults to bring you the final video in our cross-site scripting (XSS) series. Learn about cookie theft, website defacement, and CSRF attacks.
The OWASP Top 10 2025 for web applications release candidate was released last week. Take a look at which categories have moved as well as one new category.
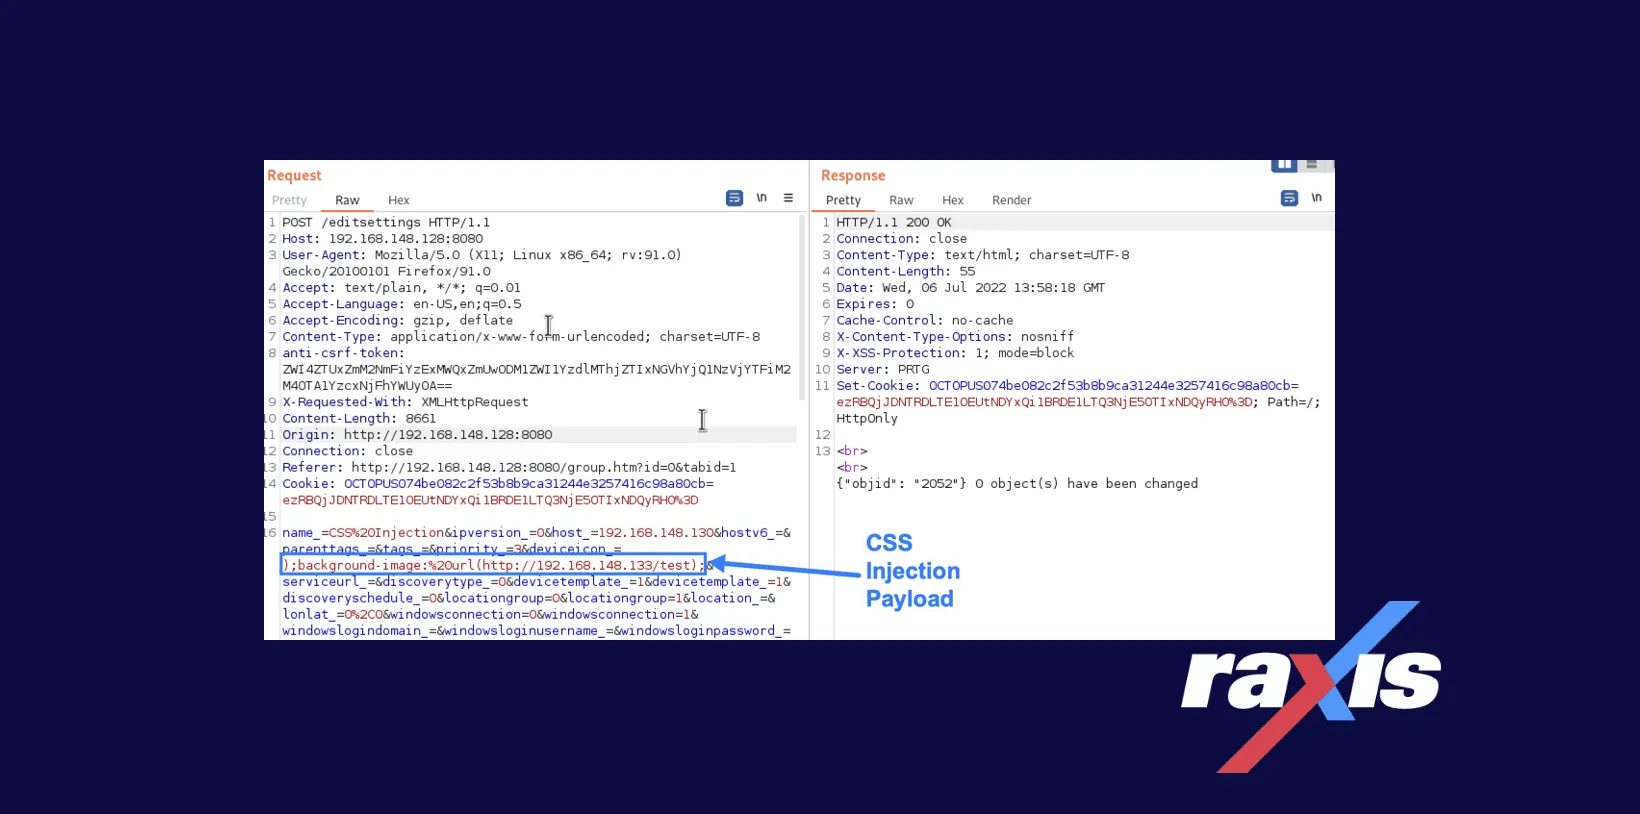
This CSS vulnerability, discovered by Raxis’ Matt Mathur, lies in a device’s properties and how they are verified and displayed within PRTG Network Monitor.
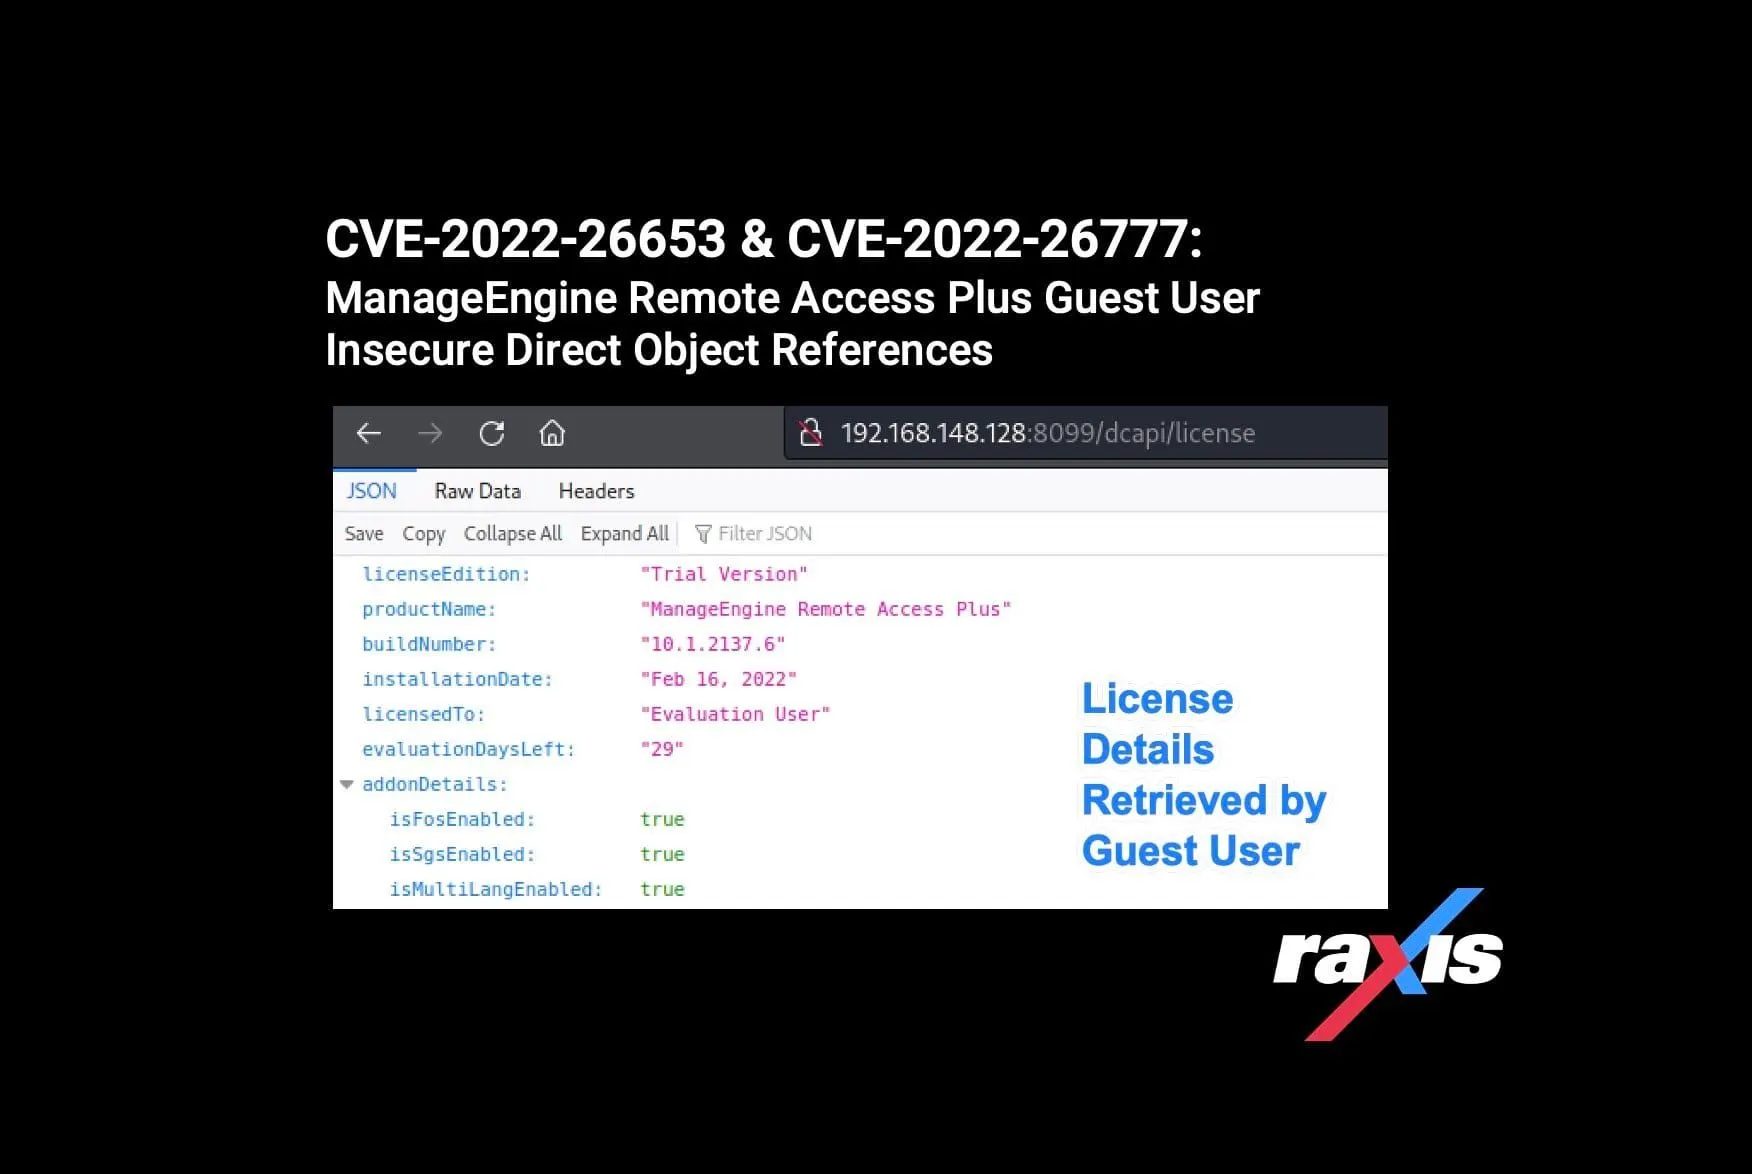
Raxis lead penetration tester Matt Dunn uncovers two more ManageEngine vulnerabilities (CVE-2022-26653 & CVE-2022-26777).
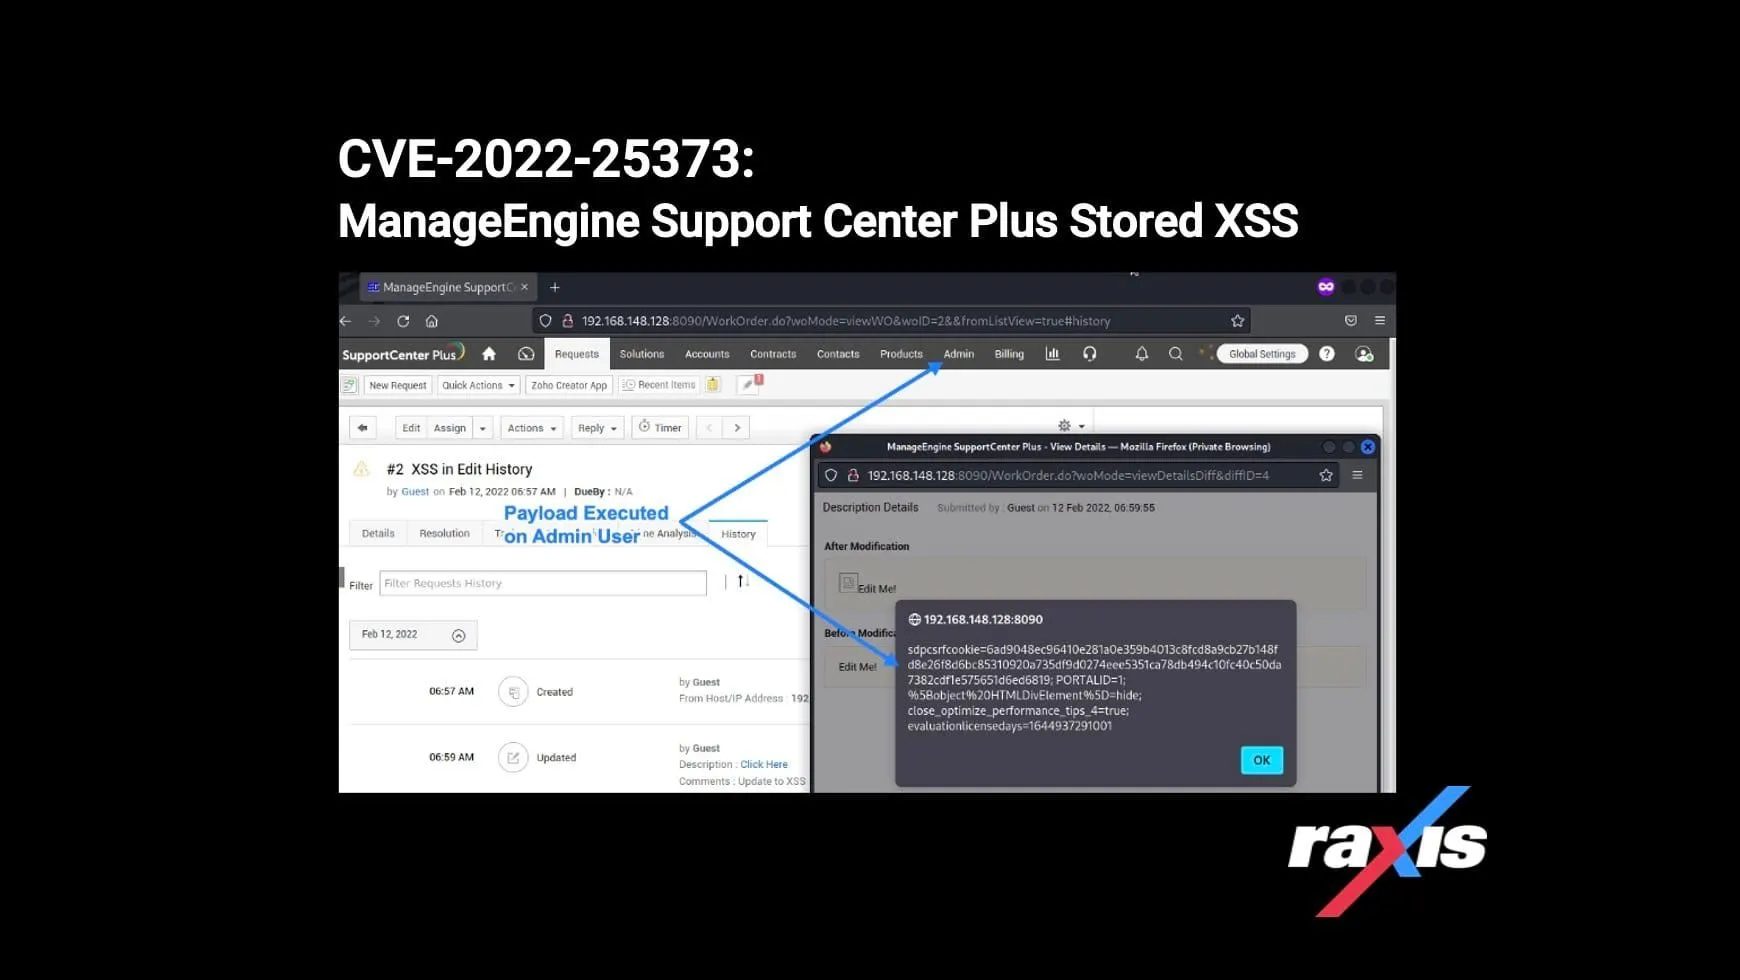
Matt Dunn discovers another ManageEngine Cross-Site Scripting vulnerability, this one in the Support Center Plus application.
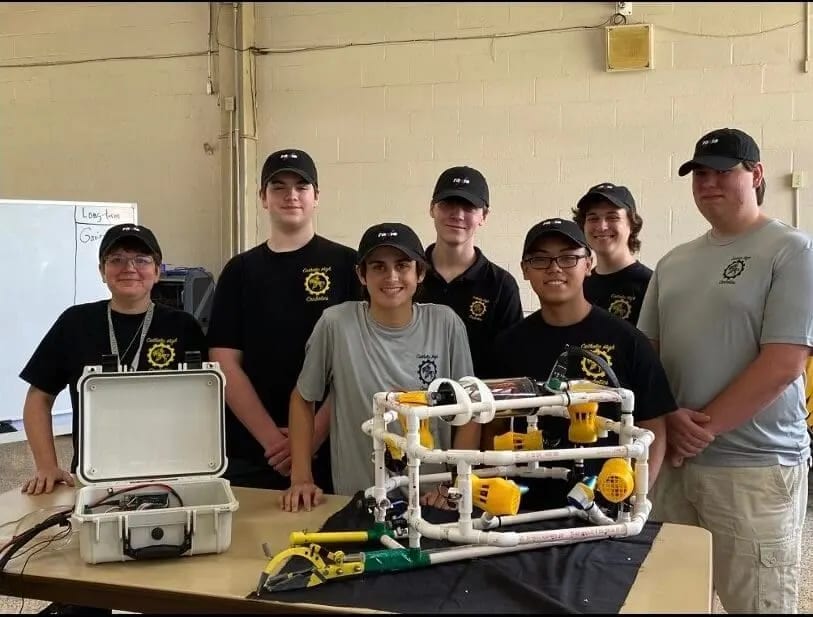
Raxis is proud to sponsor the Pensacola Catholic High School “Crubotics” robotics team. Its members will compete in June 2022’s World Championships in Long Beach, California. The event is part the MATE ROV competioton
Raxis lead penetration tester Matt Dunn discovers an information leakage vulnerability in ManageEngine’s Asset Explorer CVE-2022-25245
Raxis’ Matt Dunn continues his prolific discovery of new CSS CVEs. This one affects ManageEngine AD SelfService Plus Stored Cross-Site Scripting.
Raxis Lead Penetration Tester Matt Dunn explains why you simultaneous sessions is a significant finding on a penetration test.
Raxis’ new marketing director, Jim McClellan, talks about the unusual career path that led from consultant to full-time team member.
Lead penetration tester Matt Dunn continues his discussion about web application testing. In Part Two, Matt explains testing as an authenticated user vs. as an unauthenticated user.
Learn how Raxis approaches web application testing and how it differs from network penetration testing. Lead penetration tester Matt Dunn explains in this post.
42 posts by Raxis Research Team.