An Inside Look at a Raxis Red Team
The Raxis Red Team Test is our top tier test that gives a true feel of what hackers could do. Curious to know more? Take a look at this short video.
Discover expert insights on the latest exploits, penetration testing tactics, and real-world vulnerabilities to strengthen your cybersecurity defenses.
The Raxis Red Team Test is our top tier test that gives a true feel of what hackers could do. Curious to know more? Take a look at this short video.
Andrew Trexler ran into issues with certipy when testing on port 443 and found that NTLMRelayx.py worked better in for those ADCS Exploits on penetration tests.
Andrew Trexler adds to his AD series with a tutorial of Active Directory Certificate Services (ADCS) misconfiguration exploits for penetration tests.
Andrew Trexler continues his AD Series with an in-depth tutorial on broadcast Attacks using NTLMRelayx, MiTM6 and Responder for penetration tests.
Exploiting GraphQL, a query language inspired by the structure & functionality of online data storage & collaboration platforms Meta, Instagram & Google Sheets.
Raxis demonstrates how to obtain a remote shell on a target system during penetration tests using a Log4j open-source exploit available to all. (CVE-2021-44228)
In the cyberworld, news of a critical vulnerability affecting OpenSSL versions 3.0 – 3.0.6 will likely be the scariest part of Halloween ’22.
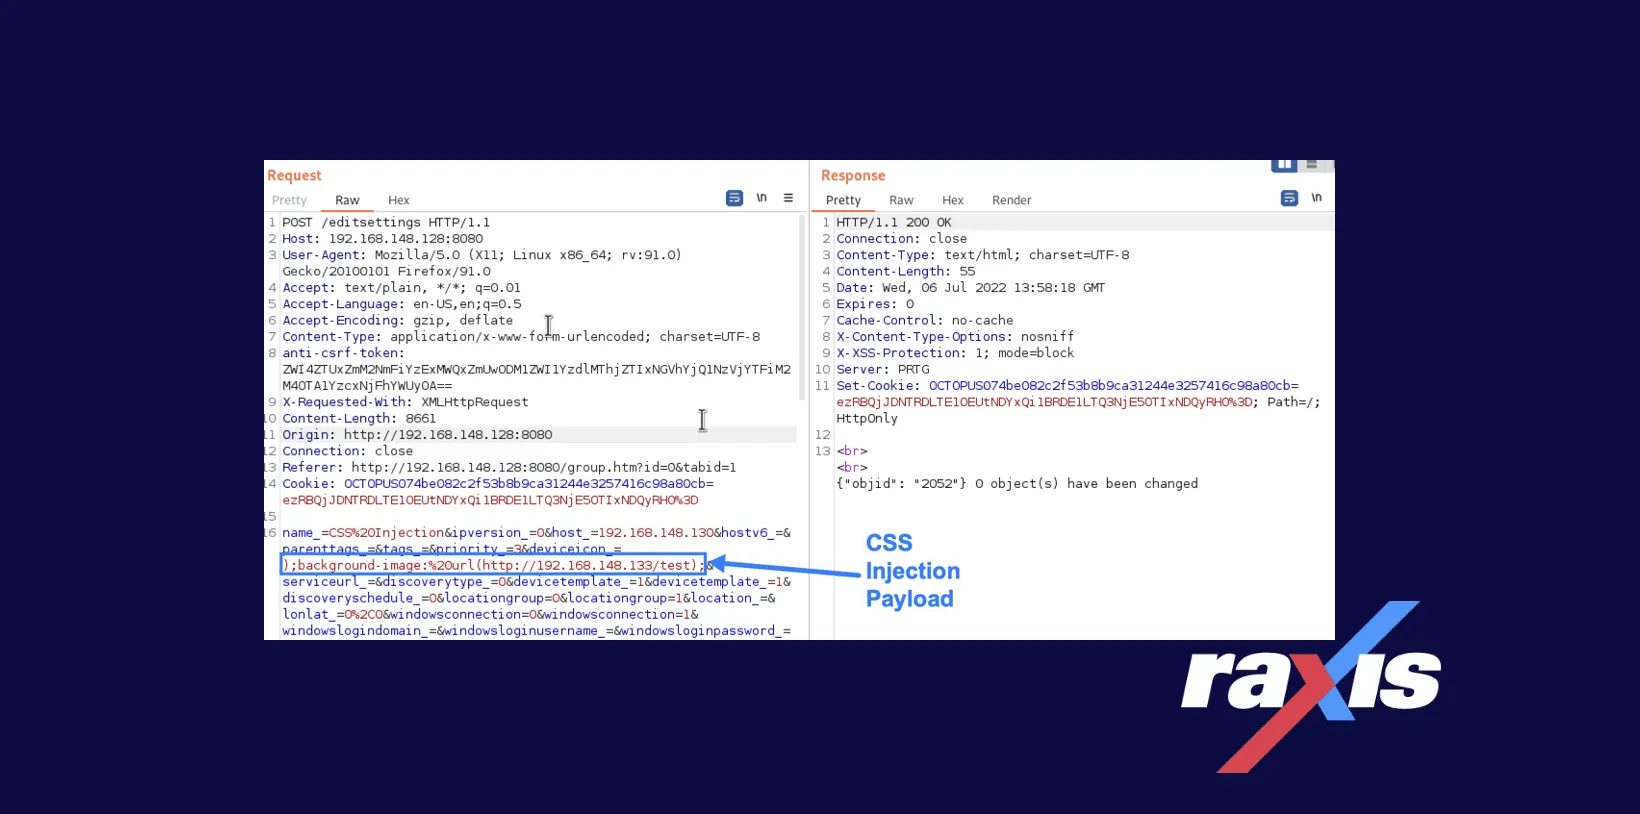
This CSS vulnerability, discovered by Raxis’ Matt Mathur, lies in a device’s properties and how they are verified and displayed within PRTG Network Monitor.
Raxis lead penetration tester Matt Dunn uncovers two more ManageEngine vulnerabilities (CVE-2022-26653 & CVE-2022-26777).
Matt Dunn discovers another ManageEngine Cross-Site Scripting vulnerability, this one in the Support Center Plus application.
Raxis lead penetration tester Matt Dunn discovers an information leakage vulnerability in ManageEngine’s Asset Explorer CVE-2022-25245
The Dirty Pipe vulnerability (CVE-2022-0847) allows any user to write to read-only files, including files that are owned by root, allowing privilege escalation.
83 posts in Exploits.