PHP2Shell and UpdraftCentral Keys: Two PHP Threats to Fix Now
Patch PHP2Shell (CVE-2026-109618, CVE-2026-109619) and remove stolen UpdraftCentral keys. Raxis explains how to check exposure and fix both PHP threats.
Get actionable cybersecurity advice from Raxis experts. Explore best practices, tips, and recommendations to strengthen your organization’s security.
Patch PHP2Shell (CVE-2026-109618, CVE-2026-109619) and remove stolen UpdraftCentral keys. Raxis explains how to check exposure and fix both PHP threats.
The French supermarket hack exploited unpatched, internet-facing Danfoss controllers. Learn why OT security gaps like this persist and how to close them.
Onsite physical pentesting includes both social aspects like tailgating and technical tests such as badge cloning. Choose a company with the whole package.
Operational Technology pentesting is highly specialized and needs to be performed by experienced OT testers. Learn how to choose the best pentest company.
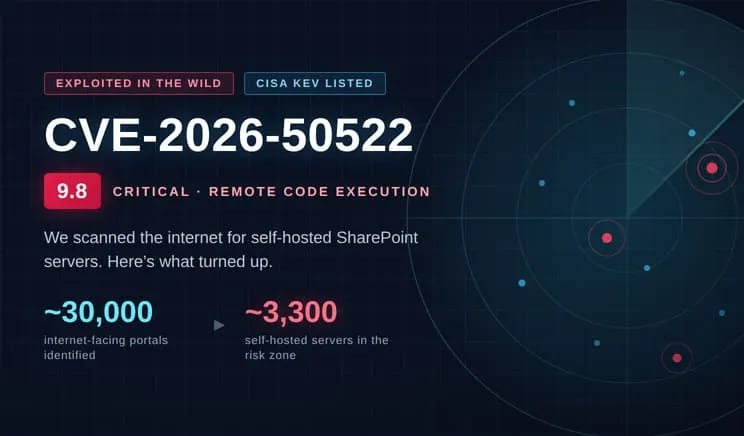
Of the nearly 30,000 public facing SharePoint portals we found, approximately 3,300 are self-hosted meaning they are vulnerable to the critical CVE-2026-50522.
It’s rare for WordPress itself to have CVEs. CVE-2026-63030 and CVE-2026-60137 combine to create the critical unauthenticated to RCE vulnerability wp2shell.
Raxis CTO Brian Tant discusses the AI portion of our annual security awareness training and how we take AI security seriously.
The new critical Microsoft Defender exploit, RoguePlanet (CVE-2026-50656), is confirmed active in the wild. Learn what it is and how to protect your network.
Large tournaments bring out fraudsters just as your employees’ guard is down. Raxis CTO Brian Tant discusses recent threats and how to protect your company.
With current local privilege escalation exploits like Copy Fail and Dirty Frag active in the wild, harden your defenses to halt attacks even before patching.
CVE-2026-0300 is a critical buffer overflow vulnerability in Palo Alto’s PAN-OS software. Discover if you are affected and what to do now.
CVE-2026-31431, dubbed Copy Fail, allows privilege escalation to root on Linux distros missing the latest kernel patches. Learn what to do in this blog.
100 posts in Security Recommendations.