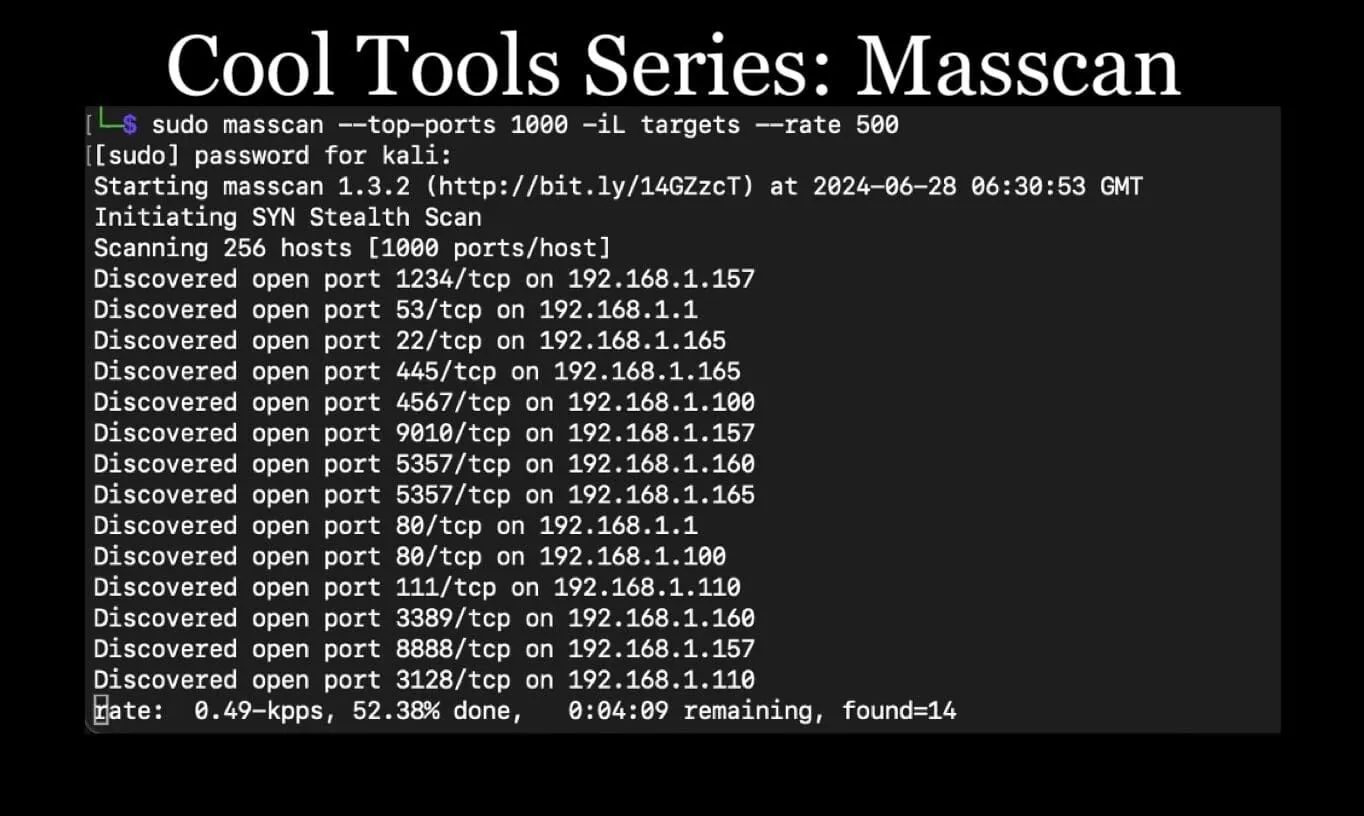
Cool Tools Series: Masscan for Penetration Testing
Continuing our Cool Tools Series, Lead Penetration Tester Andrew Trexler shows how to use masscan for discovery scanning on large networks in penetration tests.
Andrew graduated from the University of Pittsburgh with a degree in Information Science where he focused on networking and security. He continued his education by obtaining the Offensive Security Certified Professional (OSCP) and the eLearnSecurity Junior Penetration Tester (eJPT) certifications. When not participating in capture the flag events, Andrew works as a pyrotechnic operator setting up and shooting firework shows in the Pittsburgh area.
Continuing our Cool Tools Series, Lead Penetration Tester Andrew Trexler shows how to use masscan for discovery scanning on large networks in penetration tests.
Raxis’ Andrew Trexler shows how useful Nuclei is for network and application penetration tests, discovering vulnerabilities such as default passwords and more.
Andrew Trexler’s SQLi Series is back, demonstrating SQL Timing Attacks using MySQL’s sleep function in Blind SQL Injection attacks for penetration testing.
Raxis’ Andrew Trexler explains what SQL Injection (SQLi) is and how to perform a simple exploit against a web app login page in penetration tests.
Exploit msDS-AllowedToActOnBehalfOfOtherIdentitity to gain administrative access in a Resource Based Constrained Delegation (RBCD) attack on penetration tests.
Andrew Trexler ran into issues with certipy when testing on port 443 and found that NTLMRelayx.py worked better in for those ADCS Exploits on penetration tests.
Andrew Trexler adds to his AD series with a tutorial of Active Directory Certificate Services (ADCS) misconfiguration exploits for penetration tests.
Andrew Trexler continues his AD Series with an in-depth tutorial on broadcast Attacks using NTLMRelayx, MiTM6 and Responder for penetration tests.
Andrew Trexler walks us through creating a simple AD test environment to test new hacks before trying them on a penetration test.
The Dirty Pipe vulnerability (CVE-2022-0847) allows any user to write to read-only files, including files that are owned by root, allowing privilege escalation.
What’s it like to earn your OSCP? Raxis senior penetration tester Andrew Trexler talks about his experience preparing for and taking the exam.
Senior penetration tester Andrew Trexler has a penchant for breaking in and blowing up. Read on to find out why both are good things.
24 posts by Andrew Trexler.