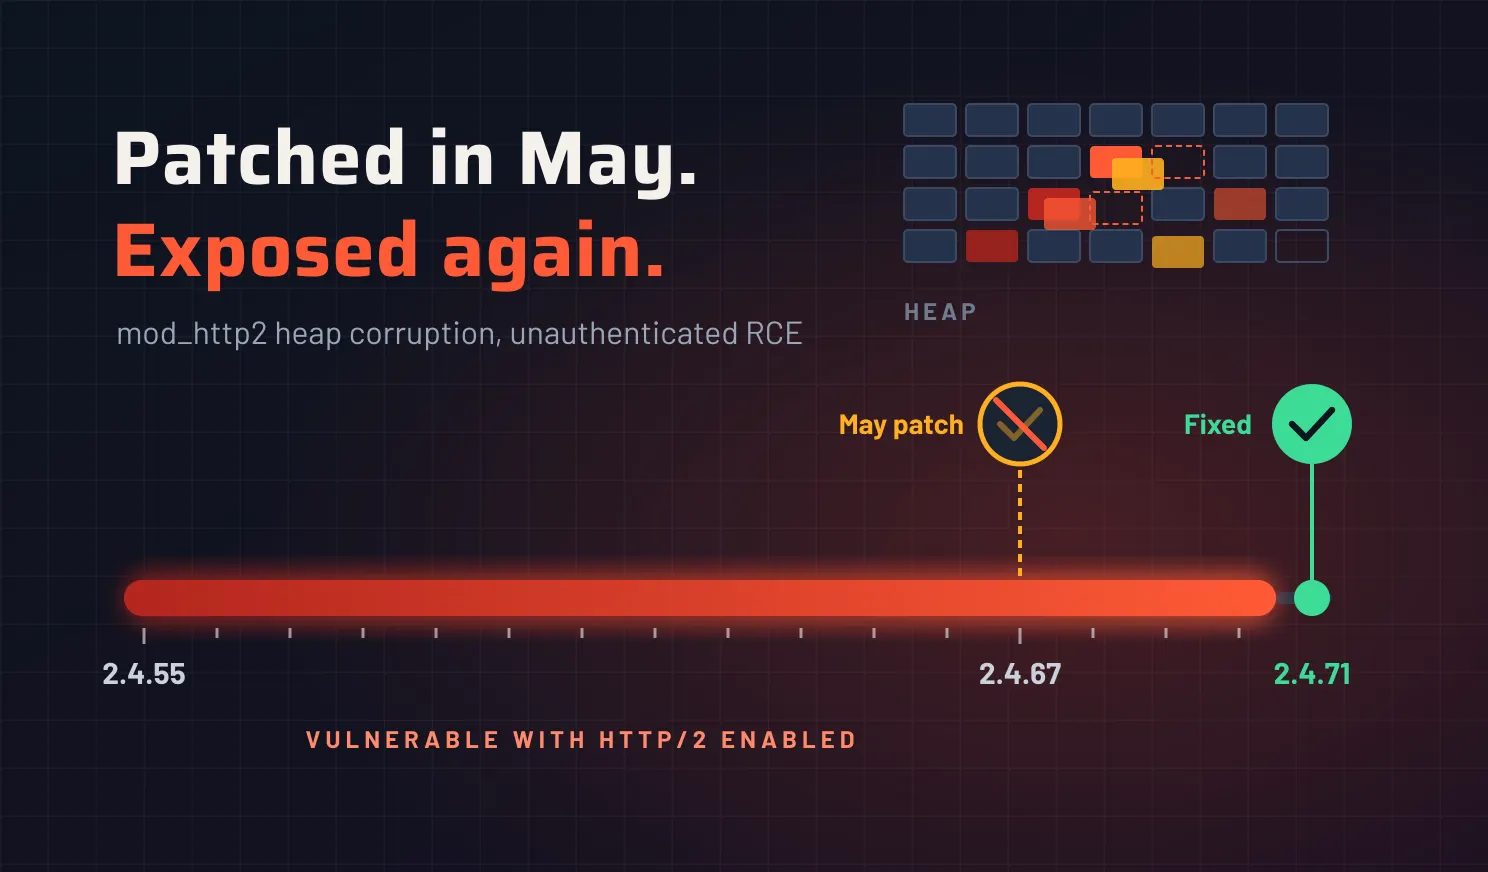
Critical Apache HTTP/2 Flaw CVE-2026-119618 – 9.8 CVSS
A critical Apache HTTP/2 flaw lets unauthenticated attackers run code on servers, even ones patched in May. Learn how to confirm exposure and mitigate it.
Scottie has over 20 years working in IT. He has experience with systems administration, networking and wireless, and security. He currently holds certifications as a GIAC Penetration Tester (GPEN) and a Certified Information Security Professional (CISSP). In his spare time, he enjoys learning new technologies, being with family, fishing and going to the beach.
A critical Apache HTTP/2 flaw lets unauthenticated attackers run code on servers, even ones patched in May. Learn how to confirm exposure and mitigate it.
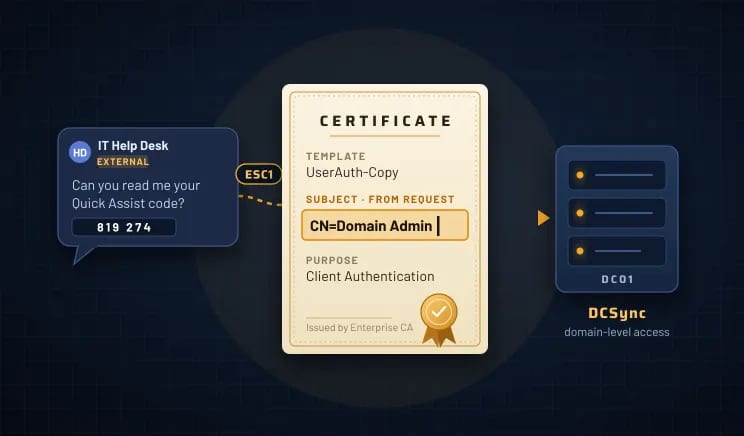
A help desk scam on Teams led to domain access through misconfigured AD CS. See how ESC1 and ESC8 work and how to close these certificate paths.
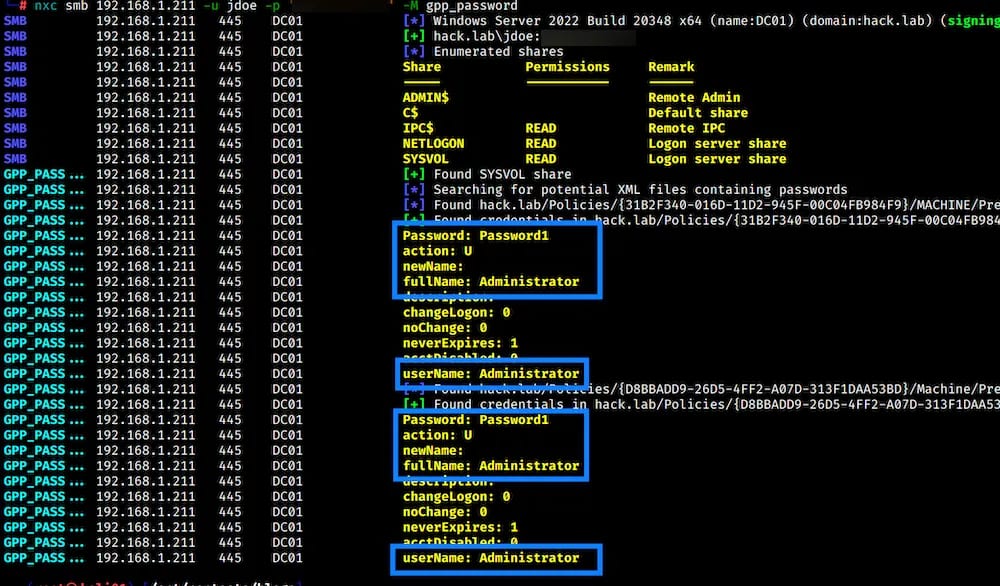
Learn how NetExec (NXC) modules speed up internal pentests. Scottie Cole covers GPP passwords, LAPS, Zerologon checks, and coerce_plus with example commands.
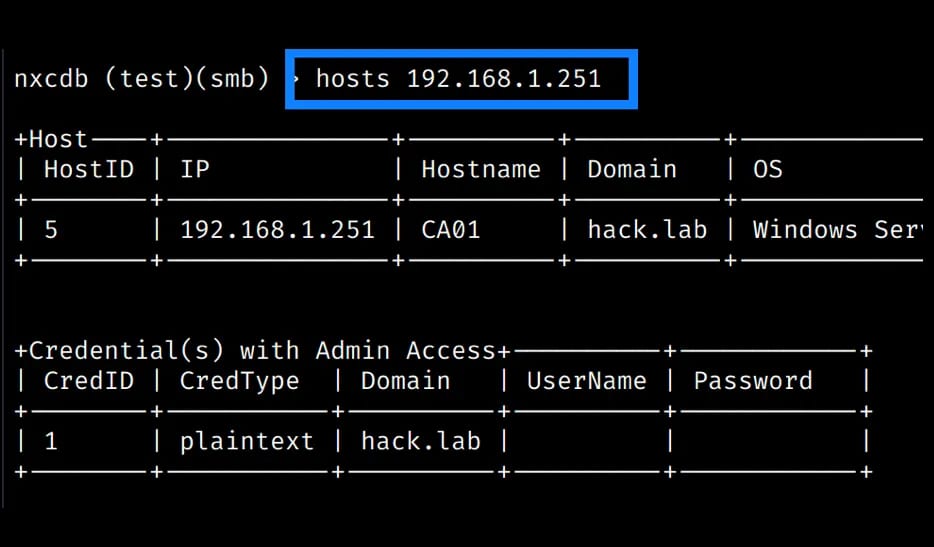
Principal Pentester Scottie Cole continues his NetExec series with nxcdb, the database that automatically stores key info like hosts and creds while you hack.
Now that CrackMapExec is no more, how is a pentester to rapidly test credentials, enumerate assets, spray passwords, and more? Learn the basics of NetExec here.
Phishing and other social engineering techniques have crossed a threshold with deepfake attacks. Scottie Cole discusses how to protect your organization.
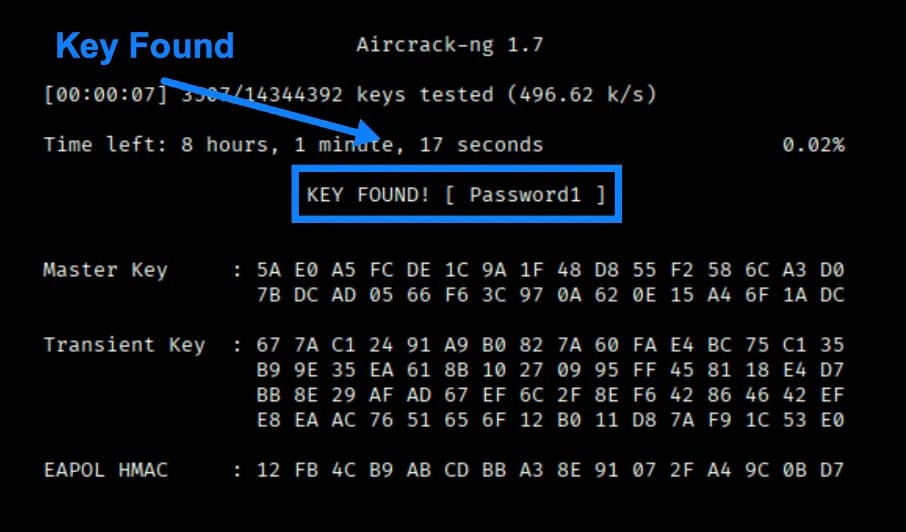
Principal Penetration Tester Scottie Cole continues our wireless series with the Aircrack-ng Suite, a set of tools for wireless pentest discovery and exploits.
Principal Penetration Tester Scottie Cole explains why Fortinet released a new security advisory about CVE‑2020‑12812 and what your organization should check.
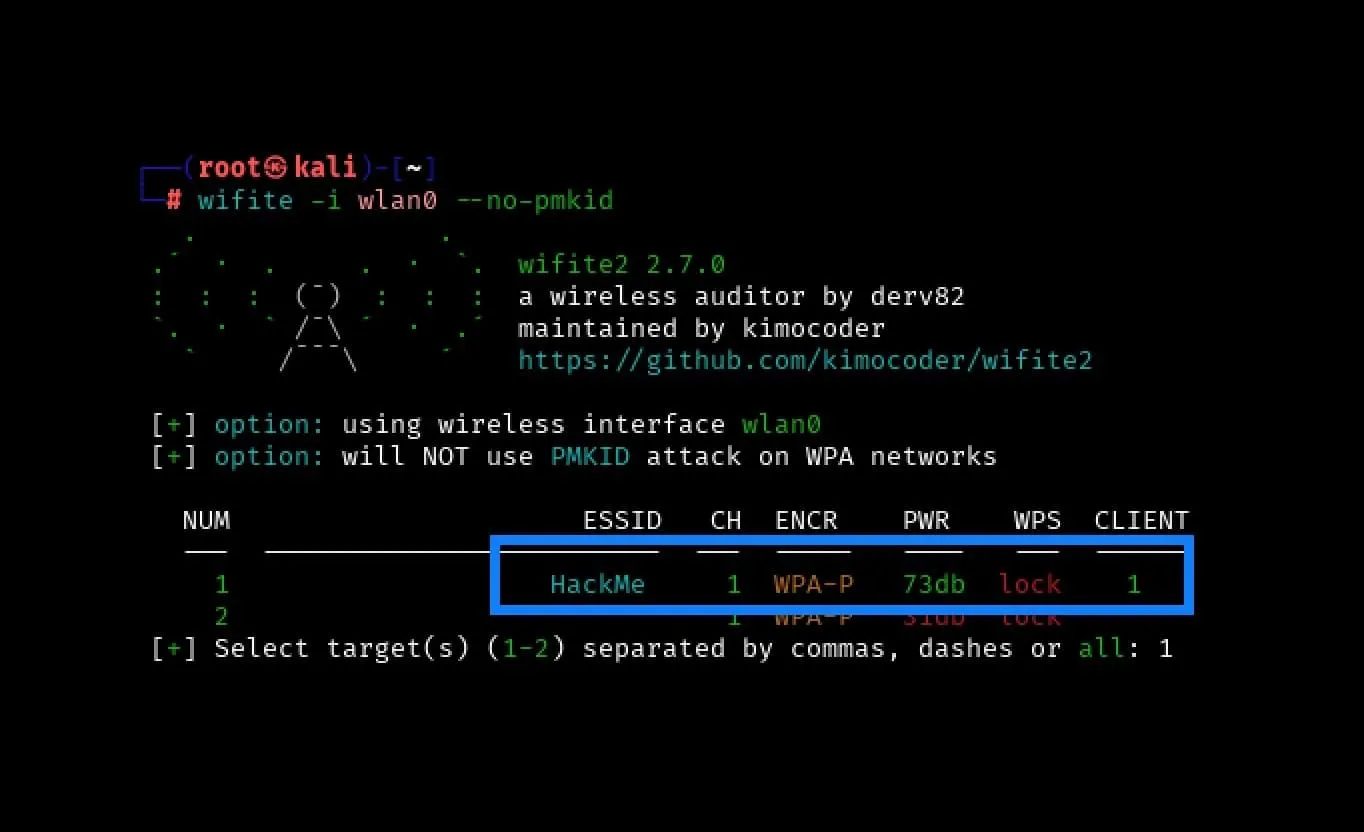
Principal Penetration Tester Scottie Cole begins our wireless penetration testing series with capturing and cracking a WPA2 Pre-Shared Key using Wifite.
Critical Alert – Patch Immediately. Cisco Releases Patch for CVE-2025-20188 – 10.0 CVSS. This vulnerability affects Cisco Catalyst 9800 wireless controllers.
Just a few days ago the world felt the rippling effects of a third-party push to networks across the globe. What would have normally been a routine undertaking instead caused mass disruption of information systems and brought businesses of all sizes to a standstill. Almost everyone was impacted by t
Raxis’ pentester, Scottie Cole, leads off our new Cool Tools Series with tips on tools for host discovery and vulnerability discovery for penetration tests.
18 posts by Scottie Cole.