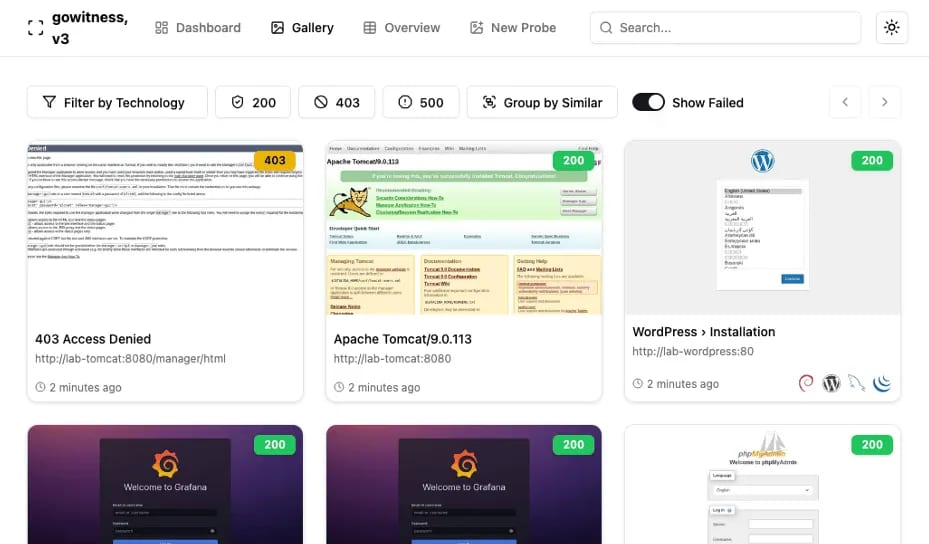
Rapid Web Host Recon with GoWitness
Enumerating webpages during an internal network pentest can be a large task, but GoWitness makes it easy to focus on high value webpages. Learn how it works.
Offensive security, written by the professionals who live it.
Enumerating webpages during an internal network pentest can be a large task, but GoWitness makes it easy to focus on high value webpages. Learn how it works.
Raxis will be at Black Hat USA 2026 August 4–6 at Mandalay Bay Convention Center in Las Vegas. Find us at booth 6018.
Raxis CTO Brian Tant discusses the AI portion of our annual security awareness training and how we take AI security seriously.
The Raxis team is serious about cybersecurity and exploits, but today we’re taking a break from that to show off our pets.
The usbliter8 SecureROM exploit is big news for jailbreaking iPhones. This hardware vulnerability cannot be fixed with a software update.
Nathan Anderson continues his Physical Social Engineering and Red Team series with the final step: looting. Learn what shows value to stakeholders in reports.
The new critical Microsoft Defender exploit, RoguePlanet (CVE-2026-50656), is confirmed active in the wild. Learn what it is and how to protect your network.
Endpoint security detects many malicious files created with pentest tools, but pentesters can sometimes bypass this by rebuilding source code. Learn how here.
Large tournaments bring out fraudsters just as your employees’ guard is down. Raxis CTO Brian Tant discusses recent threats and how to protect your company.
BloodHound’s Community Edition has everything a penetration tester needs to enumerate relationships in a domain in order to gain more access, even Domain Admin.
Raxis Lead Pentester Jason Taylor recently discovered CVE-2026-36748, a high-risk XSS vulnerability in Rock RMS that allows privilege escalation to admin.
With current local privilege escalation exploits like Copy Fail and Dirty Frag active in the wild, harden your defenses to halt attacks even before patching.
293 posts, newest first.