
Dev’s Fast Reporting of Phish Reduced Impact on Blockchain Malware Attacks
A recent successful phish allowed attackers to run malware targeting cryptocurrency transactions on various blockchains, but fast reporting limited the damage.
Offensive security, written by the professionals who live it.
A recent successful phish allowed attackers to run malware targeting cryptocurrency transactions on various blockchains, but fast reporting limited the damage.
Lead Penetration Tester Nathan Anderson provides tips on using croc for secure data exfiltration just like he does on red team engagements.
Lead Penetration Tester Ryan Chaplin walks us through 5 real-world attack scenarios used in real-world penetration tests by Raxis.
We love to hear that our cybersecurity services have been useful to our customers. See how a specialized device test was just that and how we can help you too.
Self-motivated, organized and enjoy listening to potential customers to help them scope penetration tests? Raxis is looking for outbound sales reps.
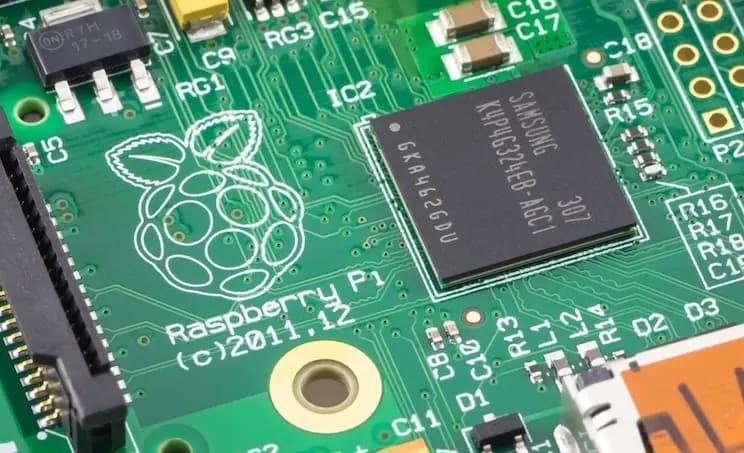
Raxis CTO Brian Tant discusses the Raspberry Pi used in a recent ATM heist and how Raxis uses the same type of device in our pentesting.
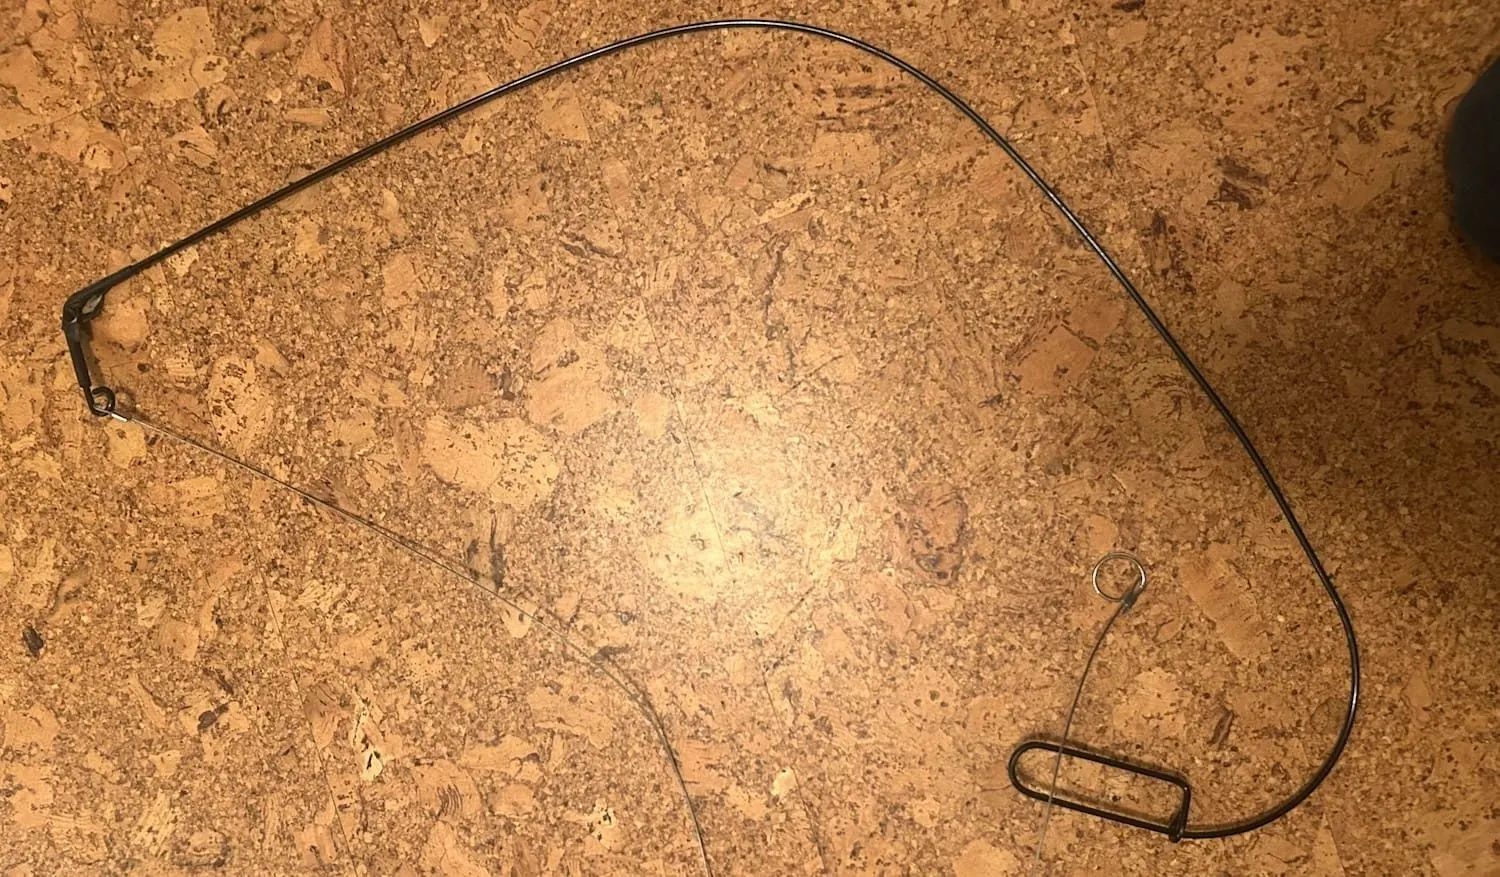
In this next post in our PSE and Red Team Series, Brad Herring explains how to use gaffer’s tape or heat-shrink tubing to make an under-door tool easier to use.
DefCon 33 has come and gone, and the Raxis team was there keeping up with cutting edge exploits for penetration tests, phishing, and PSE.
Caroline Kelly concludes our three-part “Choosing a Penetration Testing Company” series with how Penetration Testing as a Service (PTaaS) provides great value.
Microsoft has released patches for two critical vulnerabilities allowing unauthenticated remote code execution that affect on-premises SharePoint installations.
Lead Penetration Tester Jason Taylor looks at OWASP’s Top 10 list for LLM applications for penetration testing as AI machine learning becomes prevalent.
Brad Herring continues our three-part “Choosing a Penetration Testing Company” series with a look at the factors to consider when choosing the best vendor.
293 posts, newest first.