
Copy Fail – Local Linux Privilege Escalation in 4 lines
CVE-2026-31431, dubbed Copy Fail, allows privilege escalation to root on Linux distros missing the latest kernel patches. Learn what to do in this blog.
Get actionable cybersecurity advice from Raxis experts. Explore best practices, tips, and recommendations to strengthen your organization’s security.
CVE-2026-31431, dubbed Copy Fail, allows privilege escalation to root on Linux distros missing the latest kernel patches. Learn what to do in this blog.
The March 2026 attack on Stryker Corporation was not Malware and did not make Ransomware demands. Instead it used compromised credentials to disrupt business.
Last week’s supply chain attack caused many users of the WordPress and Joomla plugin Smart Slider 3 Pro to inadvertently patch to a malicious version.
With Reynolds Ransomware in the wild, Brian Tant dives into BYOVD attacks, how they evade enterprise defense like EDRs, and what your organization can do.
When a Raxis pentester Jason Taylor found a suspicious sponsored search result, he broke down the code it would have run and discovered it was malware.
Raxis has discovered and cracked our fair share of password hashes. Some that we have discovered may surprise you… and their bosses. Learn what not to do.
Reynolds poses a new type of threat by including a Bring Your Own Vulnerable Driver (BYOVD) in the ransomware bundle, making it harder for EDR tools to catch.
While BeyondTrust patched cloud-hosted Remote Support customers earlier this month, on-premises deployments of BeyondTrust must manually patch to remediate.
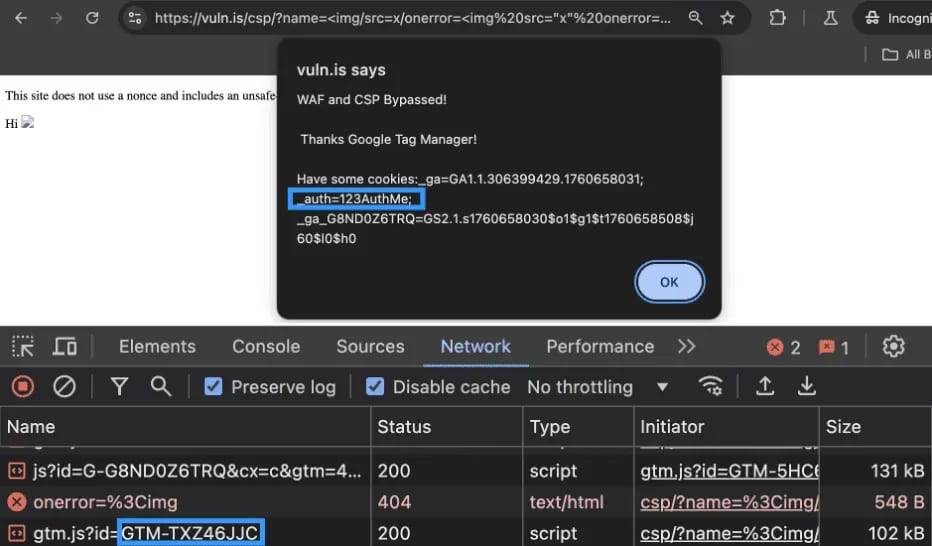
Ryan Chaplin takes an in-depth look at how attackers can use unsafe directives to bypass CSP, notably in Google Tag Manager, and how to remediate the issue.
With exploit code available for the vulnerabilities in Eaton’s xComfort Ethernet Communication Interface, Jason Taylor recommends replacing or isolating.
Andrew Trexler looks at a recently discovered public database of stolen usernames and passwords and what you can do now to protect your access and information.
Recent attacks, including GitVenom and Lumma Stealer, underscore the threat of Attackers using GitHub repositories as malware staging mechanisms.
101 posts in Security Recommendations.