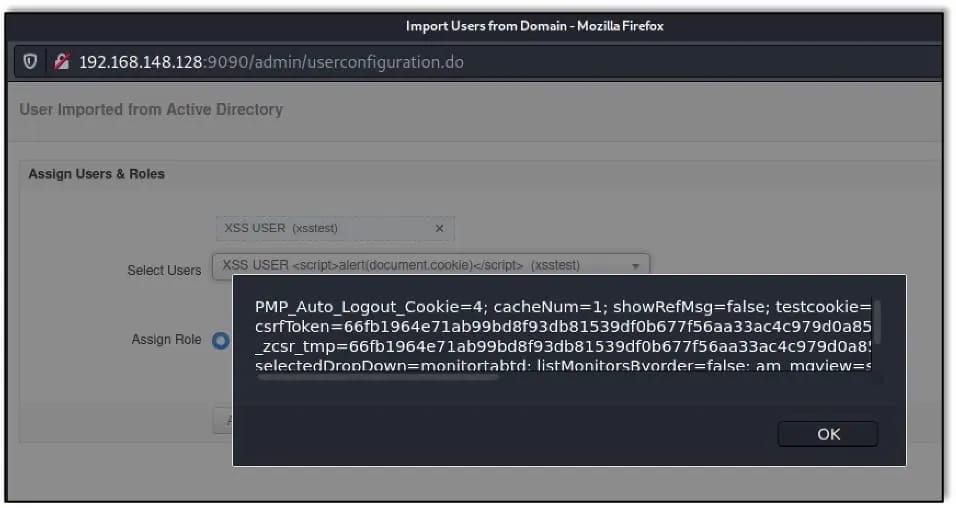
Raxis’ Matt Dunn has discovered another ManangeEngine cross-site scripting (XSS) vulnerability, this time in the Applications Manager product (CVE-2021-31813).
Is the threat of full-scale retaliation enough to prevent large-scale cyberattacks? Raxis’ Bonnie Smyre explains why this Cold War strategy is not effective.
The US government is warning businesses to beware of vulnerabilities being exploited by the Russian Foreign Intelligence Service (SVR RF). But that’s not the only group taking advantage. Here’s what you should do.
Account enumeration reveals whether usernames are valid for use in other attacks. Lead Penetration Tester Matt Dunn explains how it works and how to prevent it.
Qualys has discovered and reported a serious vulnerability (CVE-2021-3156) affecting the sudo utility. Patches are now available and Raxis recommends applying them immediately.
Cisco releases patches for some critical and high-severity vulnerabilities. Learn about the vulnerabilities and patches from the Raxis penetration testing team.
Raxis uses cookies to measure how the site is used and to connect your visit with our team
when you reach out. Necessary cookies always run. Change your choice any time from Cookie
settings in the footer. See our Privacy Policy.