
BYOVD Attacks and EDR Evasion: Why Your Endpoint Security May Not Be Enough
With Reynolds Ransomware in the wild, Brian Tant dives into BYOVD attacks, how they evade enterprise defense like EDRs, and what your organization can do.
Offensive security, written by the professionals who live it.
With Reynolds Ransomware in the wild, Brian Tant dives into BYOVD attacks, how they evade enterprise defense like EDRs, and what your organization can do.
When a Raxis pentester Jason Taylor found a suspicious sponsored search result, he broke down the code it would have run and discovered it was malware.
Raxis has discovered and cracked our fair share of password hashes. Some that we have discovered may surprise you… and their bosses. Learn what not to do.
On a recent web app pentest, Andrew Trexler used AI to find client-side code that stopped his brute-force attack then used AI again to thwart that code.
Principal Penetration Tester Scottie Cole continues our wireless series with the Aircrack-ng Suite, a set of tools for wireless pentest discovery and exploits.
Reynolds poses a new type of threat by including a Bring Your Own Vulnerable Driver (BYOVD) in the ransomware bundle, making it harder for EDR tools to catch.
While BeyondTrust patched cloud-hosted Remote Support customers earlier this month, on-premises deployments of BeyondTrust must manually patch to remediate.
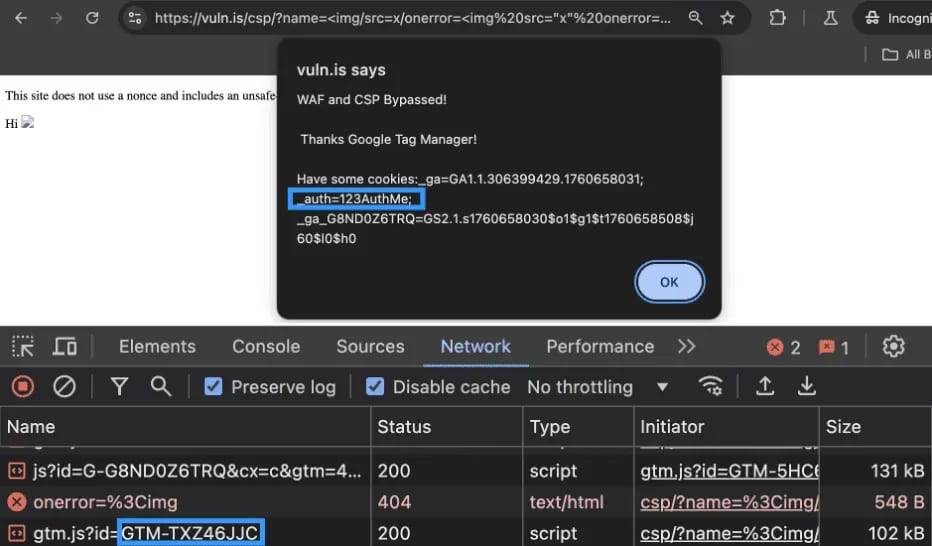
Ryan Chaplin takes an in-depth look at how attackers can use unsafe directives to bypass CSP, notably in Google Tag Manager, and how to remediate the issue.
With exploit code available for the vulnerabilities in Eaton’s xComfort Ethernet Communication Interface, Jason Taylor recommends replacing or isolating.
Andrew Trexler looks at a recently discovered public database of stolen usernames and passwords and what you can do now to protect your access and information.
Lead Penetration Tester Nathan Anderson is back with more PSE and red team tips, including tailgating, impersonating, and pretexts to gain onsite access.
Recent attacks, including GitVenom and Lumma Stealer, underscore the threat of Attackers using GitHub repositories as malware staging mechanisms.
293 posts, newest first.