Raxis at DefCon 2025
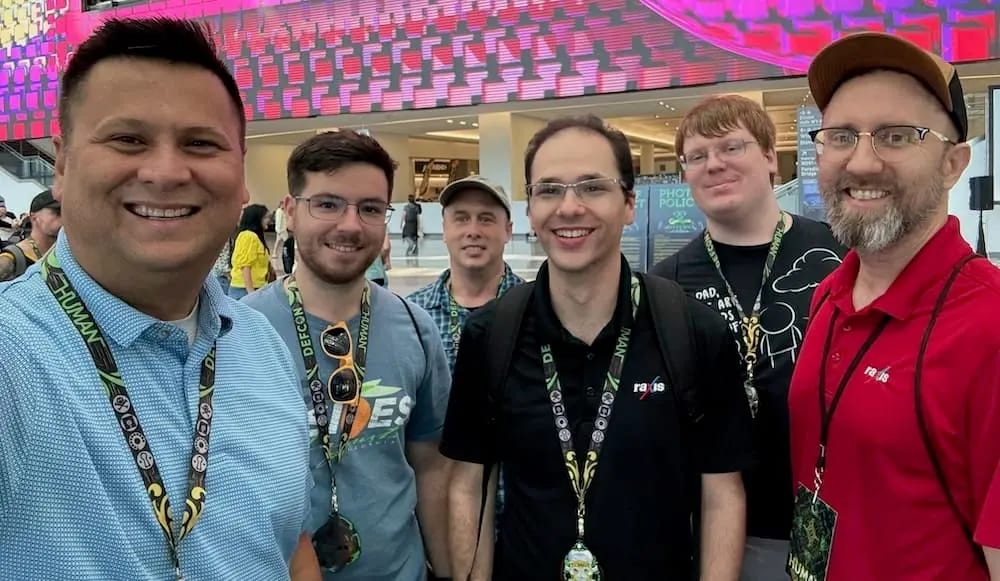
DefCon 33 has come and gone, and the Raxis team was there keeping up with cutting edge exploits for penetration tests, phishing, and PSE.
Offensive security, written by the professionals who live it.
DefCon 33 has come and gone, and the Raxis team was there keeping up with cutting edge exploits for penetration tests, phishing, and PSE.
Caroline Kelly concludes our three-part “Choosing a Penetration Testing Company” series with how Penetration Testing as a Service (PTaaS) provides great value.
Microsoft has released patches for two critical vulnerabilities allowing unauthenticated remote code execution that affect on-premises SharePoint installations.
Lead Penetration Tester Jason Taylor looks at OWASP’s Top 10 list for LLM applications for penetration testing as AI machine learning becomes prevalent.
Brad Herring continues our three-part “Choosing a Penetration Testing Company” series with a look at the factors to consider when choosing the best vendor.
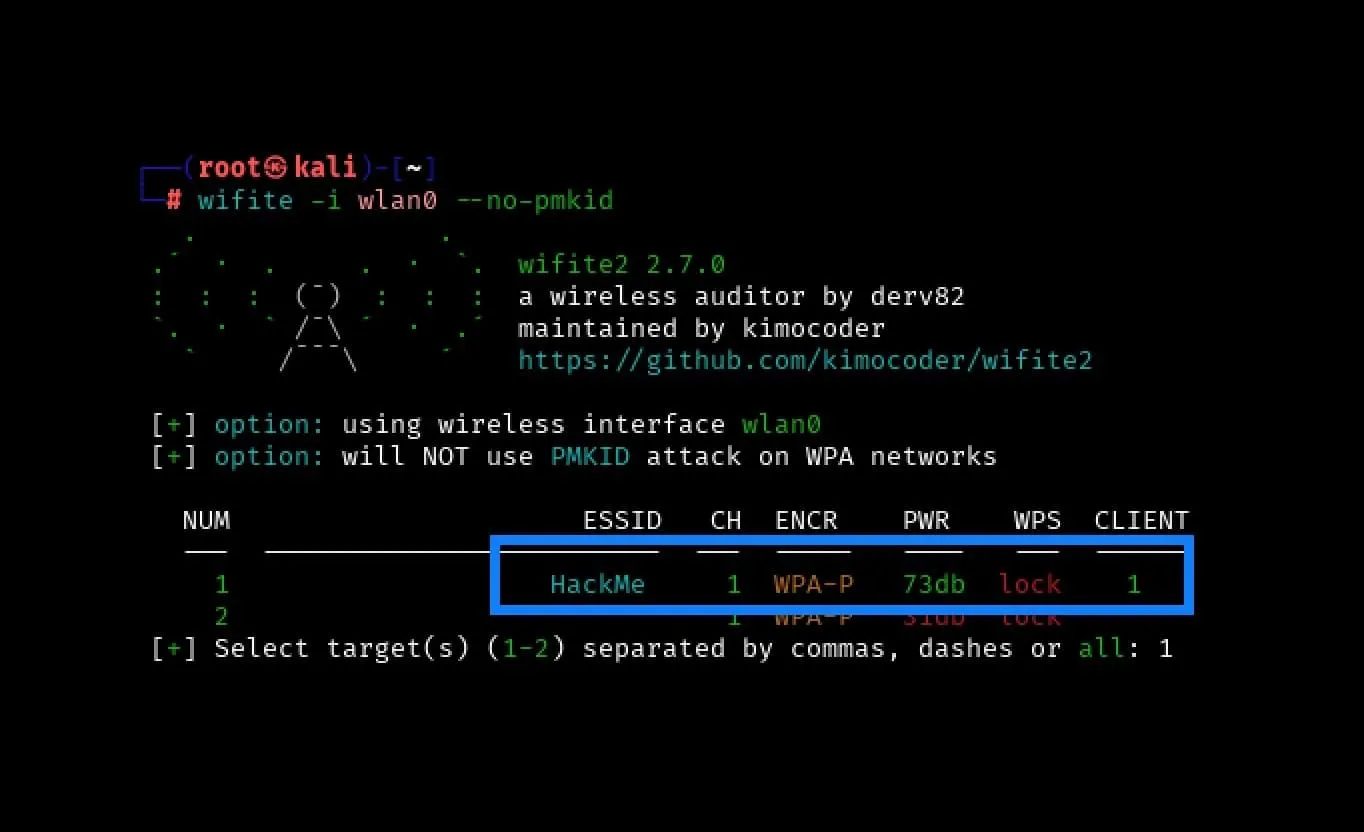
Principal Penetration Tester Scottie Cole begins our wireless penetration testing series with capturing and cracking a WPA2 Pre-Shared Key using Wifite.
Lead Penetration Tester Jason Taylor takes us step-by-step through jailbreaking an iPad 7 for use in penetration testing.
Chris Krautheim, software developer, brings skills and teamwork from his time on Georgia Tech’s drumline and computer science classes to Raxis.
Critical Alert – Patch Immediately. Cisco Releases Patch for CVE-2025-20188 – 10.0 CVSS. This vulnerability affects Cisco Catalyst 9800 wireless controllers.
Principal Penetration Tester Andrew Trexler got curious how easy it might be to customize a phish to a specific website using AI. The answer? Very easy.
Cole Stafford starts our three-part “Choosing a Penetration Testing Company” series by looking at what penetration testing is and the types of penetration tests.
Raxis lead penetration tester, Nathan Anderson, continues our PSE & Red Team series with a discussion on the tools and techniques to bypass entry controls.
298 posts, newest first.