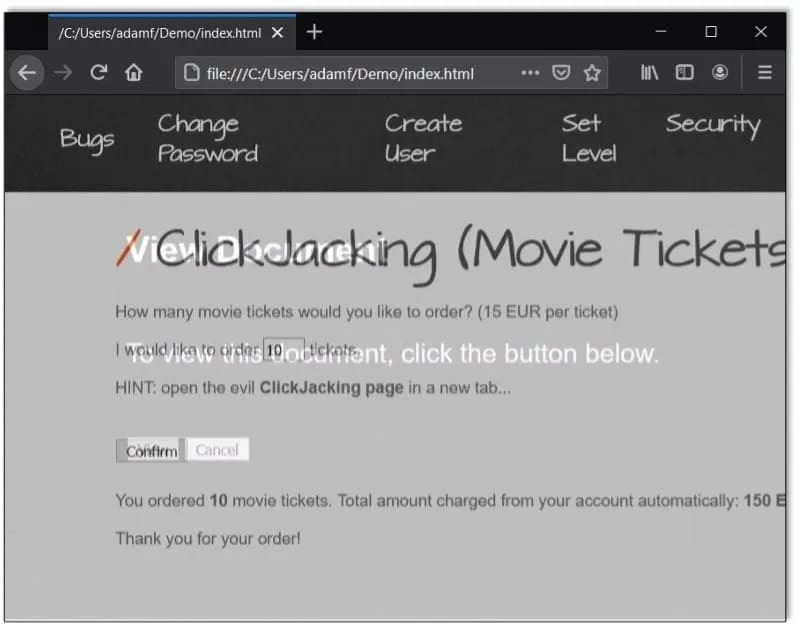
Raxis’ Lead Developer Adam Fernandez discusses clickjacking, explaining what it is and why it represents less of a threat now than it once did. Adam also talks about how clickjacking differs from similar attacks.
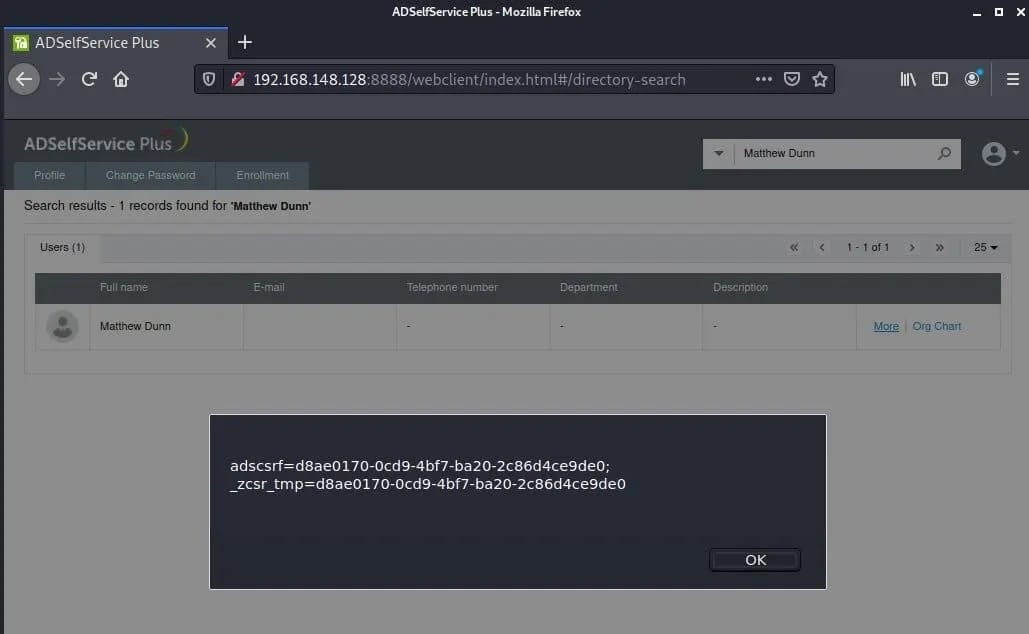
Raxis lead penetration tester Matt Dunn has uncovered a new cross-site scripting vulnerability in Manage Engine AD Self Service Plus (CVE-2021-27956). Find out more here.
Is the threat of full-scale retaliation enough to prevent large-scale cyberattacks? Raxis’ Bonnie Smyre explains why this Cold War strategy is not effective.
LDAP passback exploits are easy when companies fail to change default passwords on network devices or fail to assign a password at all. If you connect it, you must protect it.
The US government is warning businesses to beware of vulnerabilities being exploited by the Russian Foreign Intelligence Service (SVR RF). But that’s not the only group taking advantage. Here’s what you should do.
Concluding our series about working for Raxis is a message from our CEO, Mark Puckett. Interested in penetration testing with an elite team? Learn more here.
Account enumeration reveals whether usernames are valid for use in other attacks. Lead Penetration Tester Matt Dunn explains how it works and how to prevent it.
Raxis uses cookies to measure how the site is used and to connect your visit with our team
when you reach out. Necessary cookies always run. Change your choice any time from Cookie
settings in the footer. See our Privacy Policy.