Raxis is now verified for Red Team Access in Anthropic’s Cyber Verification Program. That gives our engineers Claude Mythos, Anthropic’s newest frontier model, cleared for authorized penetration testing.
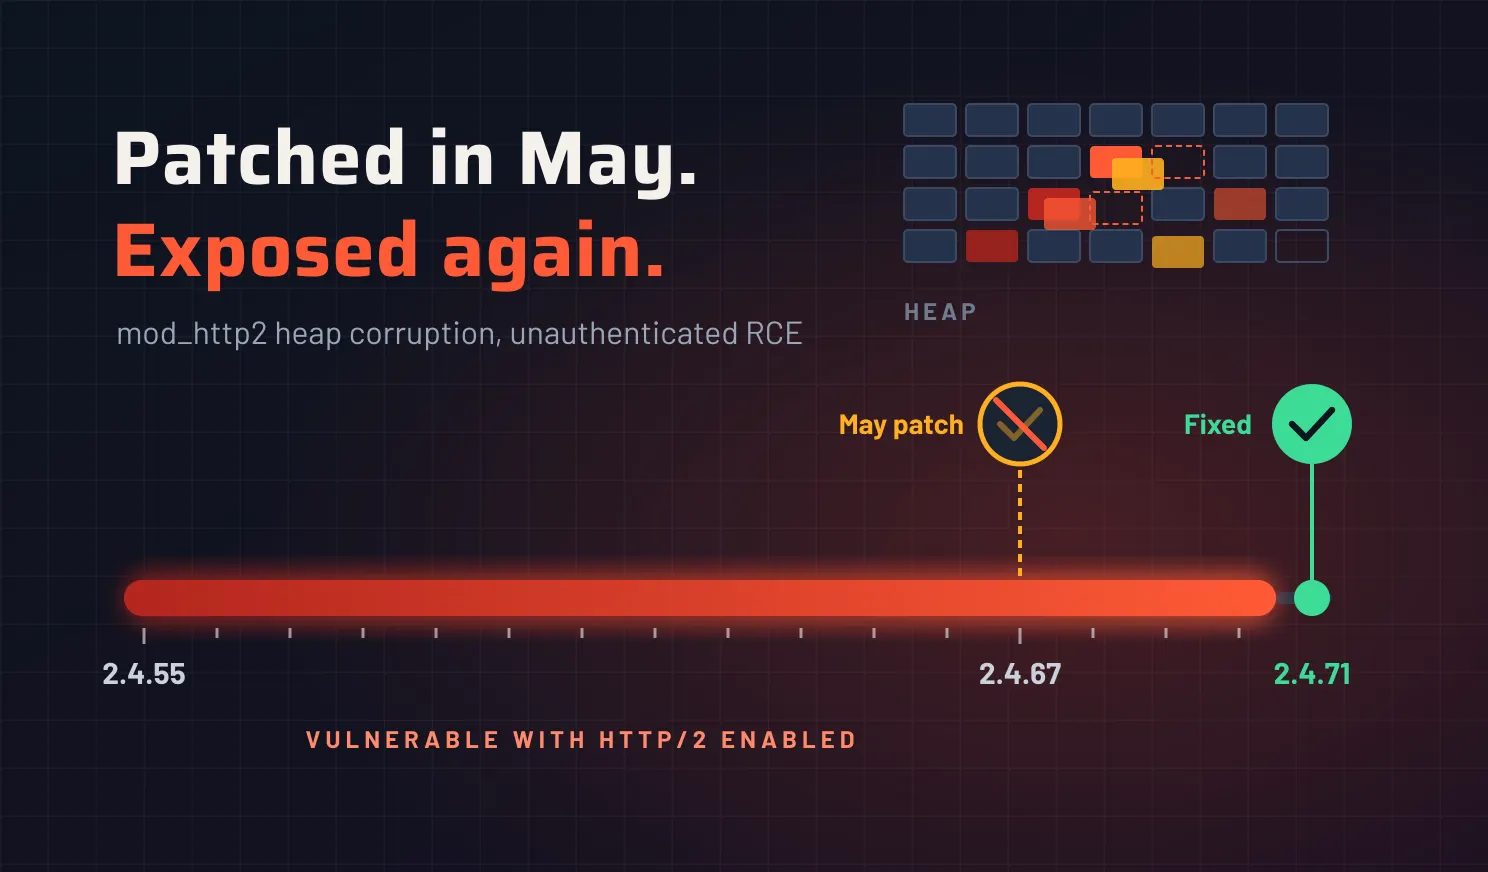
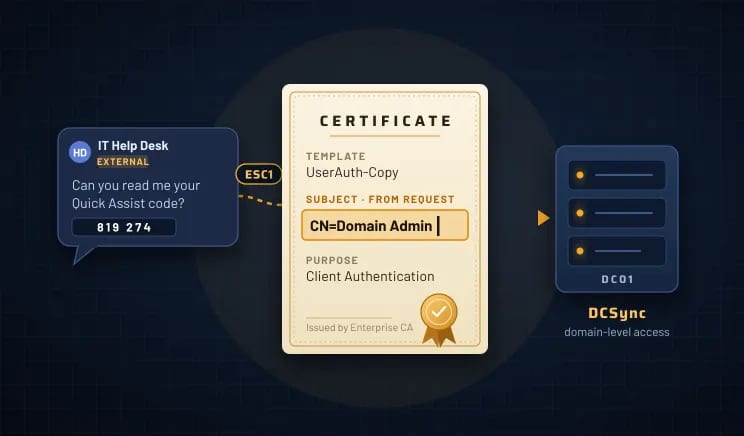
A critical Apache HTTP/2 flaw lets unauthenticated attackers run code on servers, even ones patched in May. Learn how to confirm exposure and mitigate it.
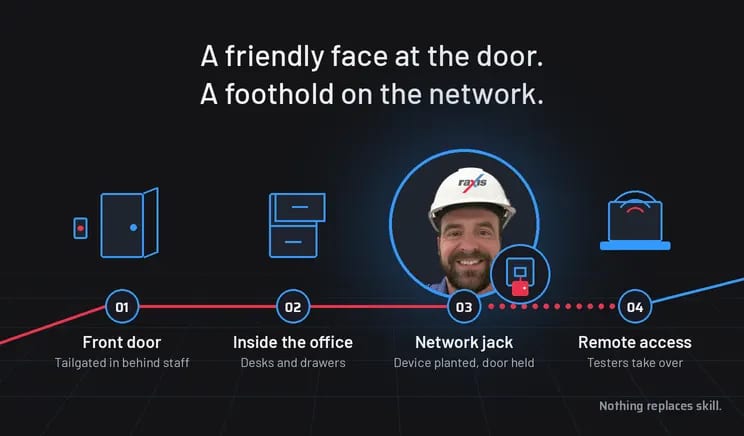
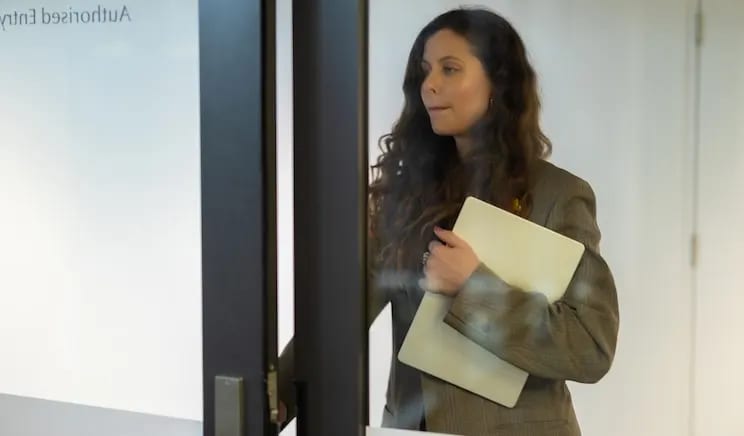
How confidence alone gets a stranger into your building, and how that access turns into a remote network foothold. Inside a real Raxis red team engagement.
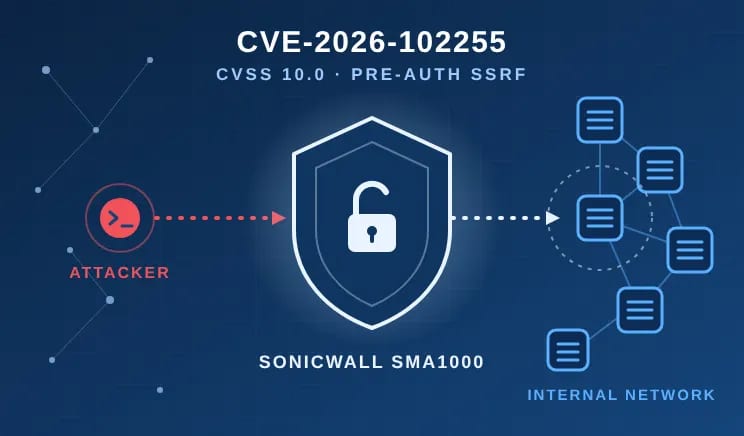
CVE-2026-102255 is a CVSS 10.0 SSRF flaw in SonicWall SMA1000 appliances. Attempts began two days after disclosure. Learn why patch windows must shrink.
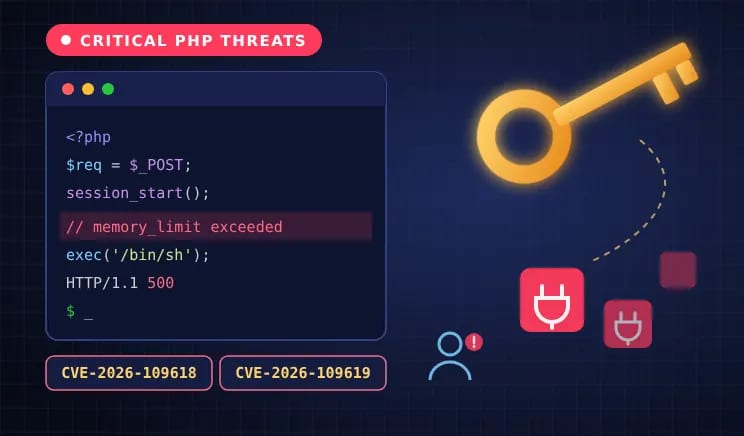
Patch PHP2Shell (CVE-2026-109618, CVE-2026-109619) and remove stolen UpdraftCentral keys. Raxis explains how to check exposure and fix both PHP threats.
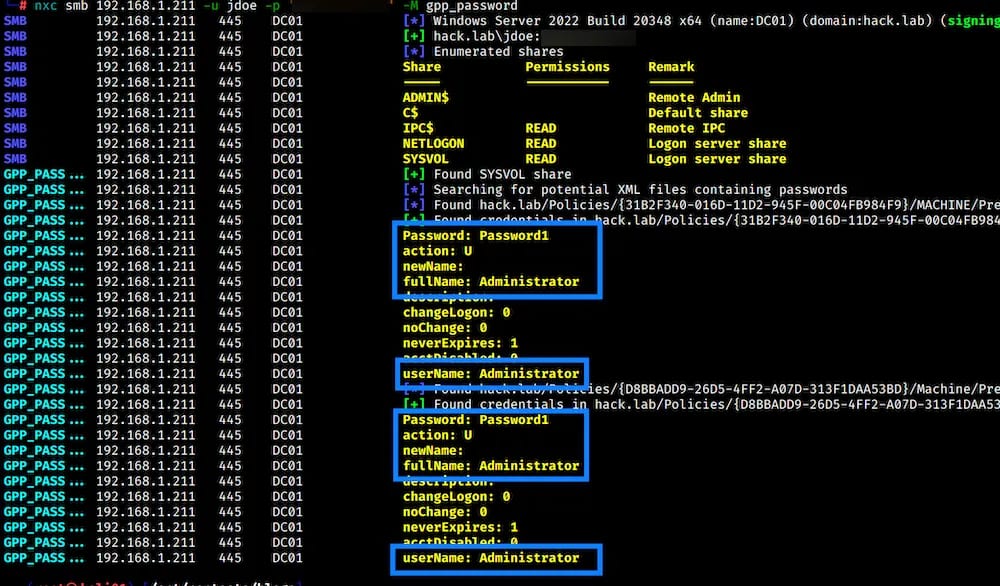
Learn how NetExec (NXC) modules speed up internal pentests. Scottie Cole covers GPP passwords, LAPS, Zerologon checks, and coerce_plus with example commands.
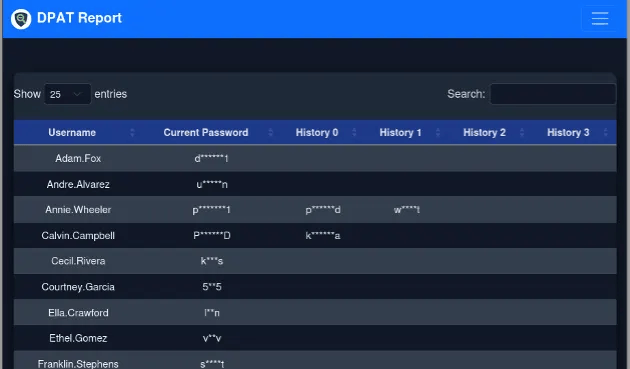
The French supermarket hack exploited unpatched, internet-facing Danfoss controllers. Learn why OT security gaps like this persist and how to close them.
With guardrails lowered, OpenAI’s AI agents chained vulnerabilities and breached Hugging Face. Here’s what the incident means for your AI and network security.
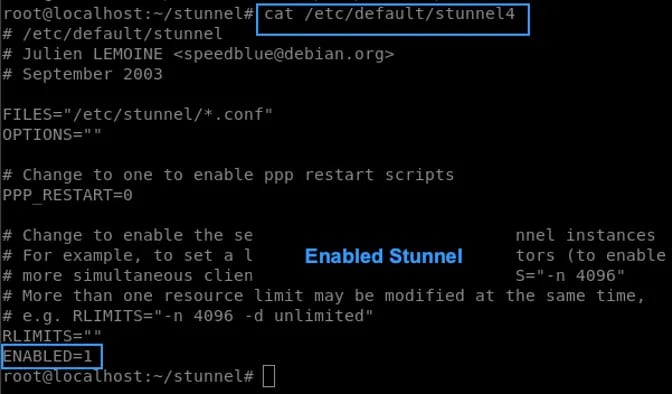
Pentesters often need to bypass Deep Packet Inspection (DPI), network IPS, and SOC detection by disguising network traffic. Learn how stunnel does just that.
Onsite physical pentesting includes both social aspects like tailgating and technical tests such as badge cloning. Choose a company with the whole package.
301 posts, newest first.
Want This Run Against Your Environment?
Talk to the engineers who write this. Real exploitation, real evidence, real fixes.
Raxis uses cookies to measure how the site is used and to connect your visit with our team
when you reach out. Necessary cookies always run. Change your choice any time from Cookie
settings in the footer. See our Privacy Policy.