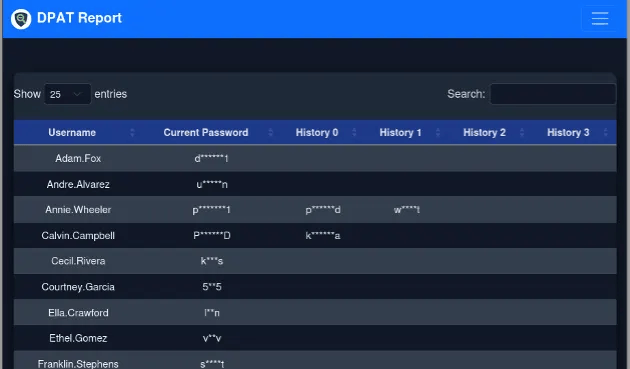
Auditing Passwords with Domain Password Audit Tool (DPAT)
Learn how to use the Domain Password Audit Tool (DPAT) that helps you discover if policies are bypassed and if new policies need to be in place.
Offensive security, written by the professionals who live it.
Learn how to use the Domain Password Audit Tool (DPAT) that helps you discover if policies are bypassed and if new policies need to be in place.
Onsite physical pentesting includes both social aspects like tailgating and technical tests such as badge cloning. Choose a company with the whole package.
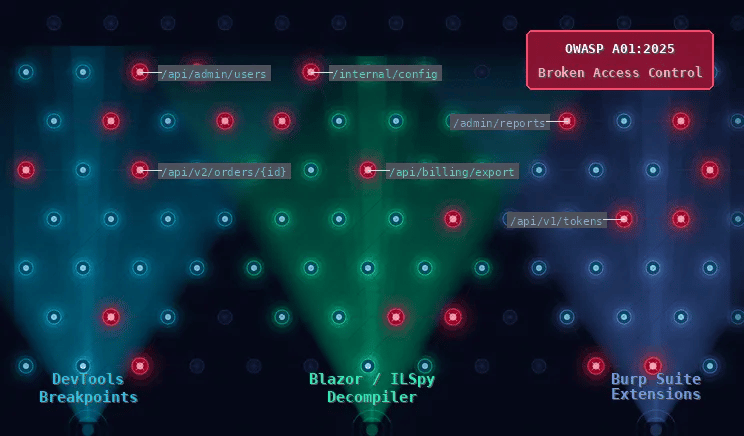
Broken Access Controls is at the top of the OWASP Top 10. The difficulty is finding each instance to test. Learn 3 ways to enumerate API endpoints thoroughly.
Operational Technology pentesting is highly specialized and needs to be performed by experienced OT testers. Learn how to choose the best pentest company.
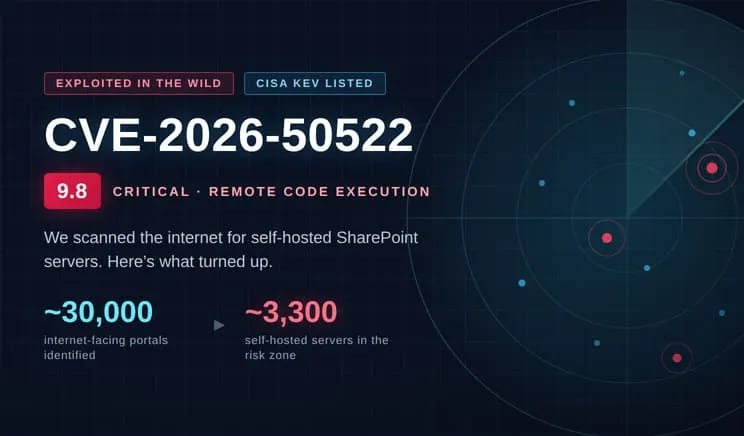
Of the nearly 30,000 public facing SharePoint portals we found, approximately 3,300 are self-hosted meaning they are vulnerable to the critical CVE-2026-50522.
Principal Penetration Tester Andrew Trexler takes us step-by-step through the process of rooting a Google Pixel for mobile application pentesting.
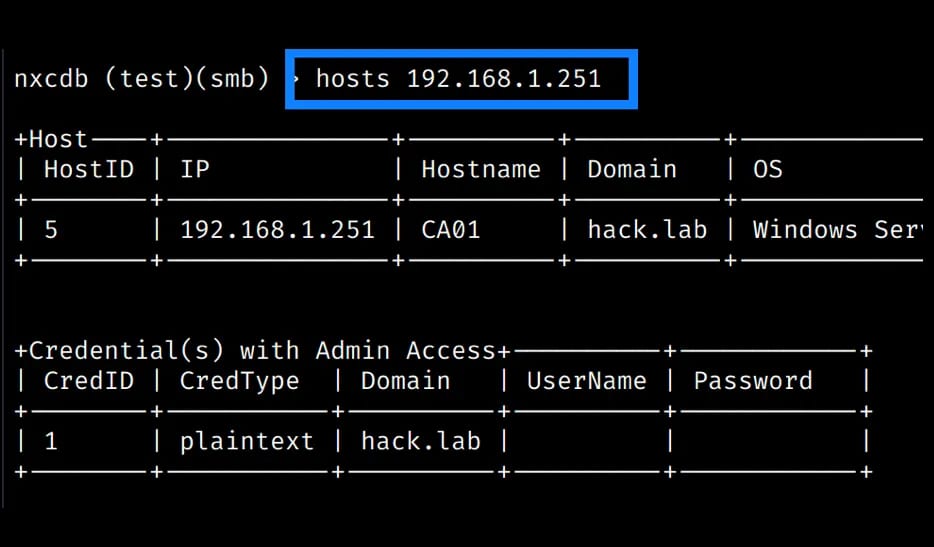
Principal Pentester Scottie Cole continues his NetExec series with nxcdb, the database that automatically stores key info like hosts and creds while you hack.
Raxis pentesters attended DEF CON 34 last weekend. The theme resonated as we see more automated pentest offerings that don’t live up to human expert testers.
Black Hat 2026 is in the books, and the Raxis team had great conversations with security-minded folks looking for senior-level human hackers and OT experts.
It’s rare for WordPress itself to have CVEs. CVE-2026-63030 and CVE-2026-60137 combine to create the critical unauthenticated to RCE vulnerability wp2shell.
Enumerating webpages during an internal network pentest can be a large task, but GoWitness makes it easy to focus on high value webpages. Learn how it works.
Raxis will be at Black Hat USA 2026 August 4–6 at Mandalay Bay Convention Center in Las Vegas. Find us at booth 6018.
292 posts, newest first.